AI Interaction Data Fabric Insights
Unauthorized ChatGPT Detection · Financial Data Upload Prevention
August 19, 2026
Shadow AI Finance FAQs
Speak to an ExpertWhat is the AI Interaction Data Fabric?
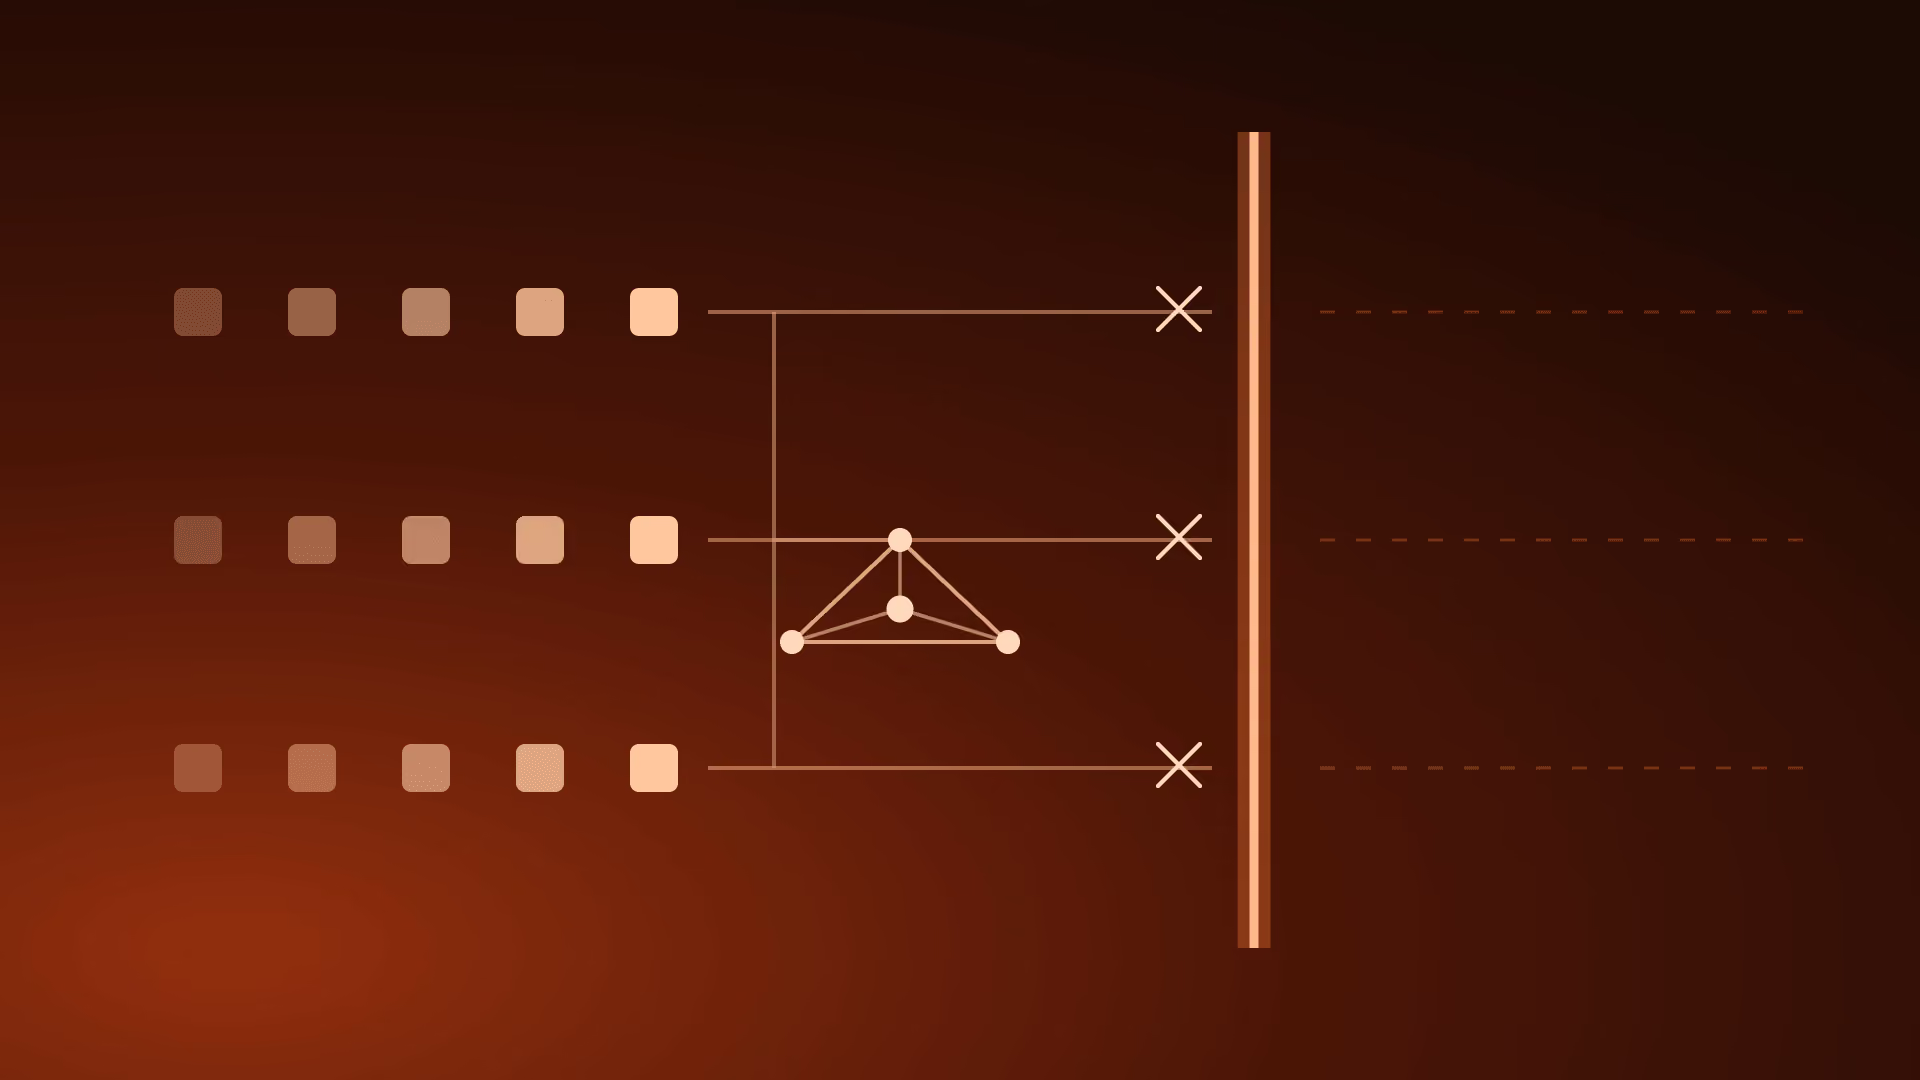
The AI Interaction Data Fabric is the layer inside Kovrr's AI Security and Governance Platform that draws telemetry from every connected source into one analytical view, spanning network, identity, browser, endpoint, cloud, and the AI Vendor Risk Catalog. Signals that each source records in isolation get triangulated into a single dated and attributed finding. Exposure that stays invisible to any one console surfaces once the sources are read against one another.
What does signal triangulation mean?
Signal triangulation is the practice of reading telemetry from several independent sources against one another rather than trusting any single log. A paste captured in the browser carries little weight alone, and an identity resolved in the directory carries little weight alone. The exposure appears only where those separate readings overlap, which turns a set of benign events into one reportable finding.
How does the AI Interaction Data Fabric detect unauthorized ChatGPT use?
A finance identity pasting classified data into a consumer AI assistant reads as ordinary web traffic to any single tool. The network sees an upload it cannot inspect, and the browser extension reads the paste without the identity behind it. The directory resolves a regulated finance identity while the vendor catalog holds a train-on-input classification for the tool, neither one seeing what the other recorded. Triangulated, the four sources establish that one regulated identity moved classified content into a tool that trains on user input and retains it, which stands as a reportable regulated-data exposure.
Why does a single security tool miss data pasted into ChatGPT?
Each tool in the stack sees one sliver of the event and reads it as ordinary. The network records an upload it cannot inspect, since the session is encrypted and the destination is a sanctioned browser. The browser extension reads the paste without the identity behind it, and the directory resolves a regulated finance identity without seeing what that identity did next. No single source holds enough to call it exposure. The event becomes reportable only where the four readings overlap, which is why one console never raises it.
