Managing AI Third-Party and Vendor Risk With Continuous Oversight
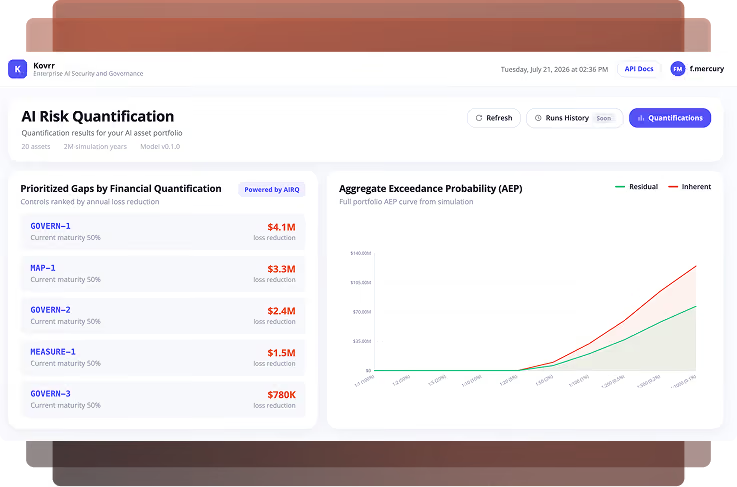
Kovrr's AI third-party risk management platform delivers continuous, data-driven visibility into how suppliers and partners deploy AI, including autonomous agents. It helps organizations map dependencies, assess vendor risk, financially quantify third-party AI exposure, and track contractual and compliance status across their extended ecosystem."


Gain Visibility Into AI Use Across Your Vendor Ecosystem
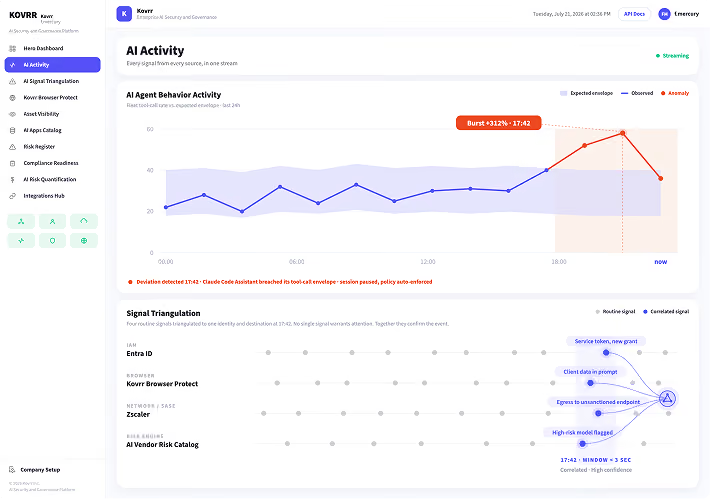
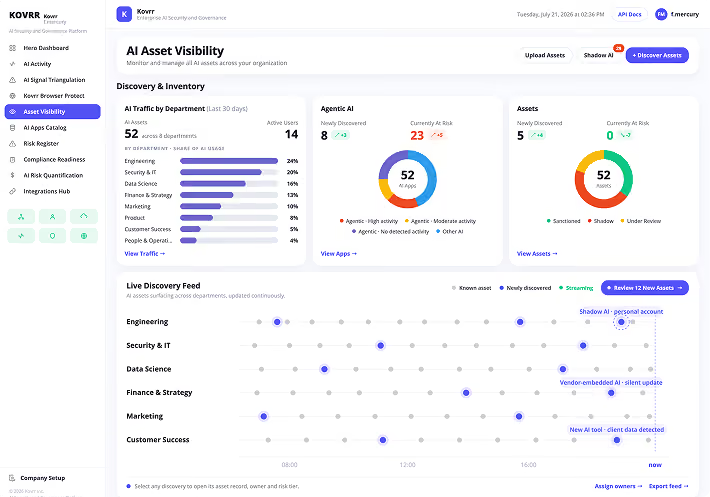
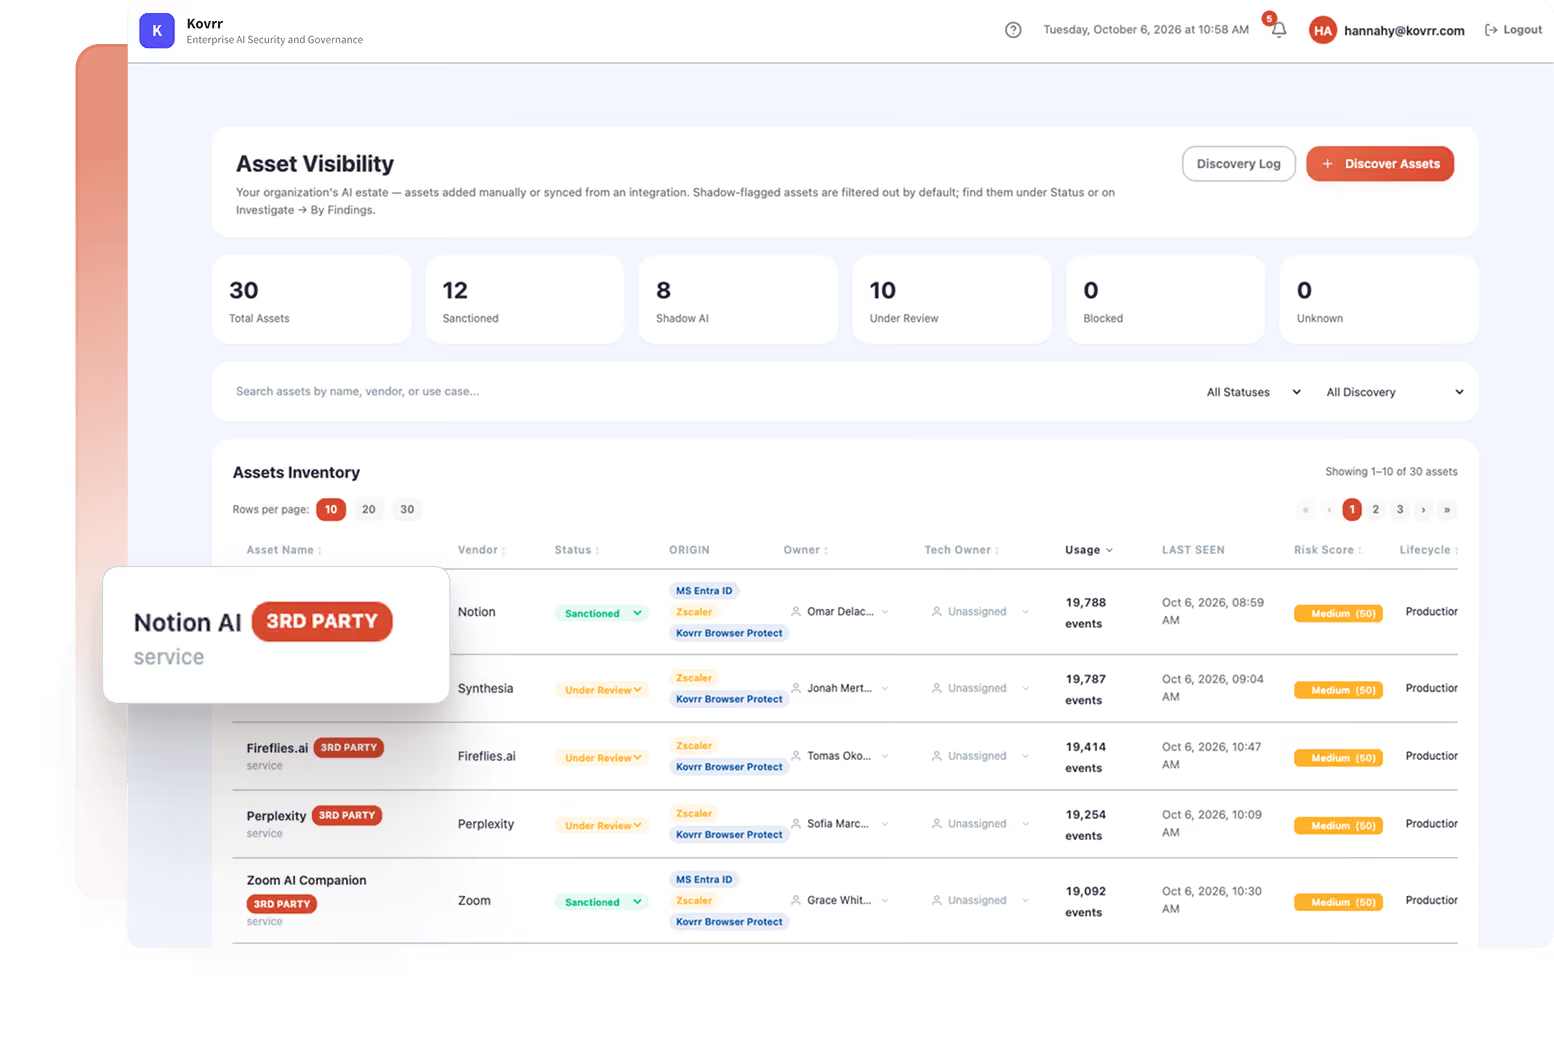
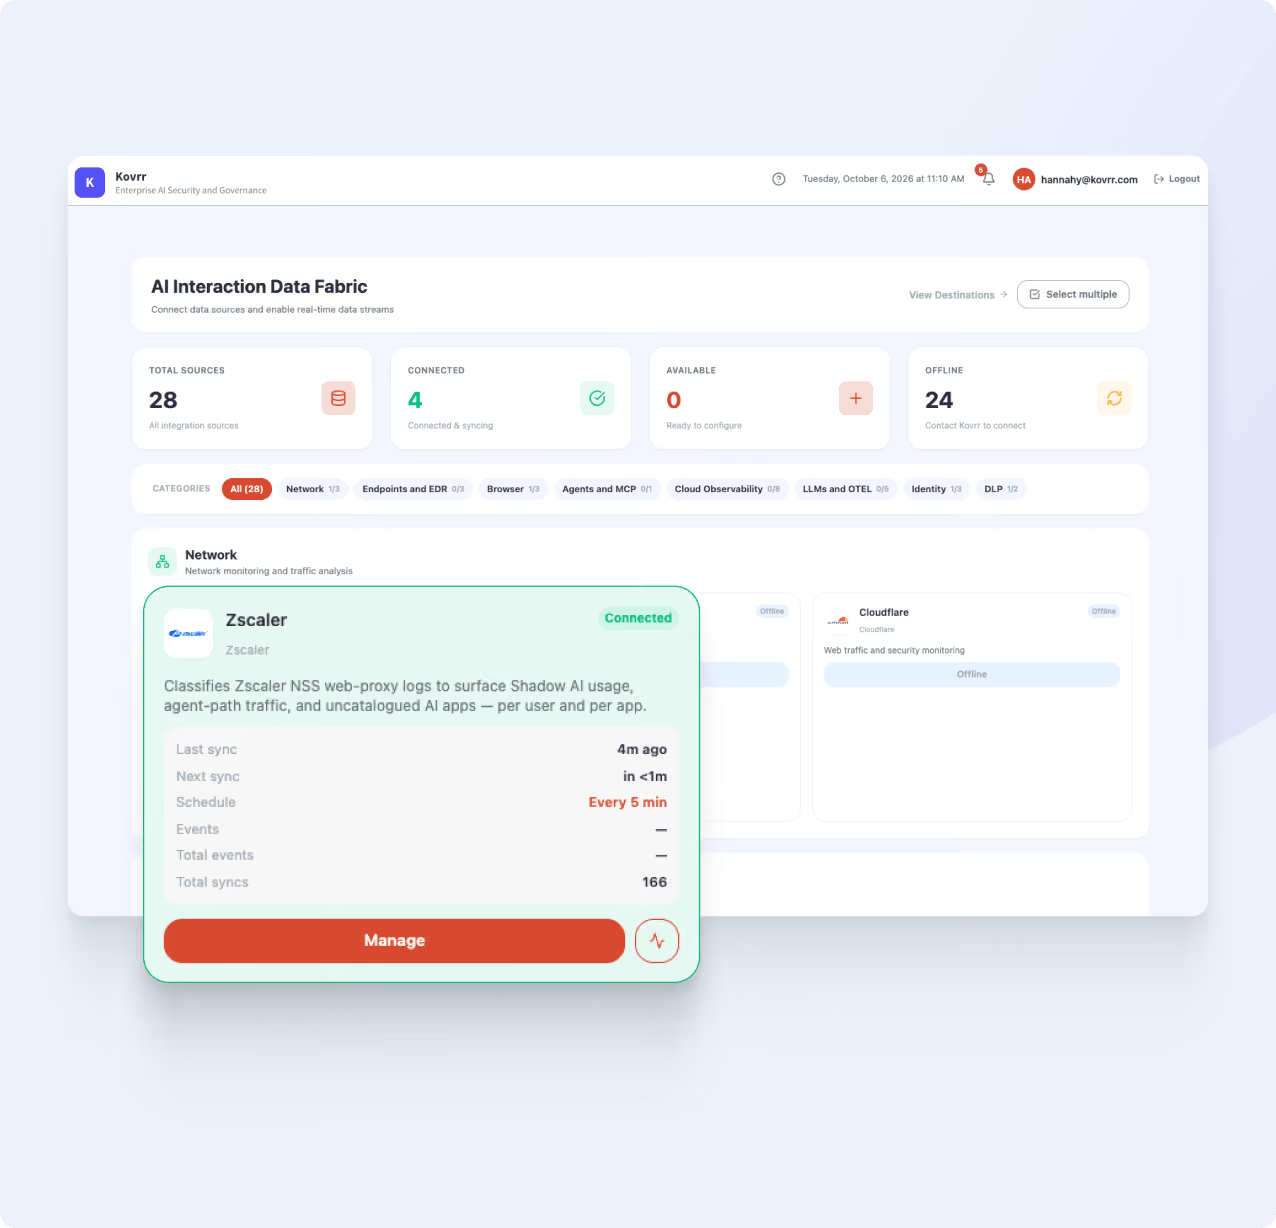
Kovrr’s AI Governance and Security Platform provides real-time insight into where and how third parties use AI and AI agents, giving organizations a full picture of exposure across their supply chain.
Identify vendors and sub-vendors using AI in high-impact or data-sensitive processes.
Map dependencies across your extended supply chain with interactive network views.
Detect unreported or high-risk AI use cases, including agentic AI deployments, among suppliers
Maintain a unified inventory of third-party AI exposure, complete with risk signals and last-assessment data.
This level of visibility eliminates hidden dependencies and ensures that AI-driven activities within your ecosystem remain transparent, measurable, and ready to inform quantified financial exposure analysis.
Evaluate Governance and Compliance Alignment
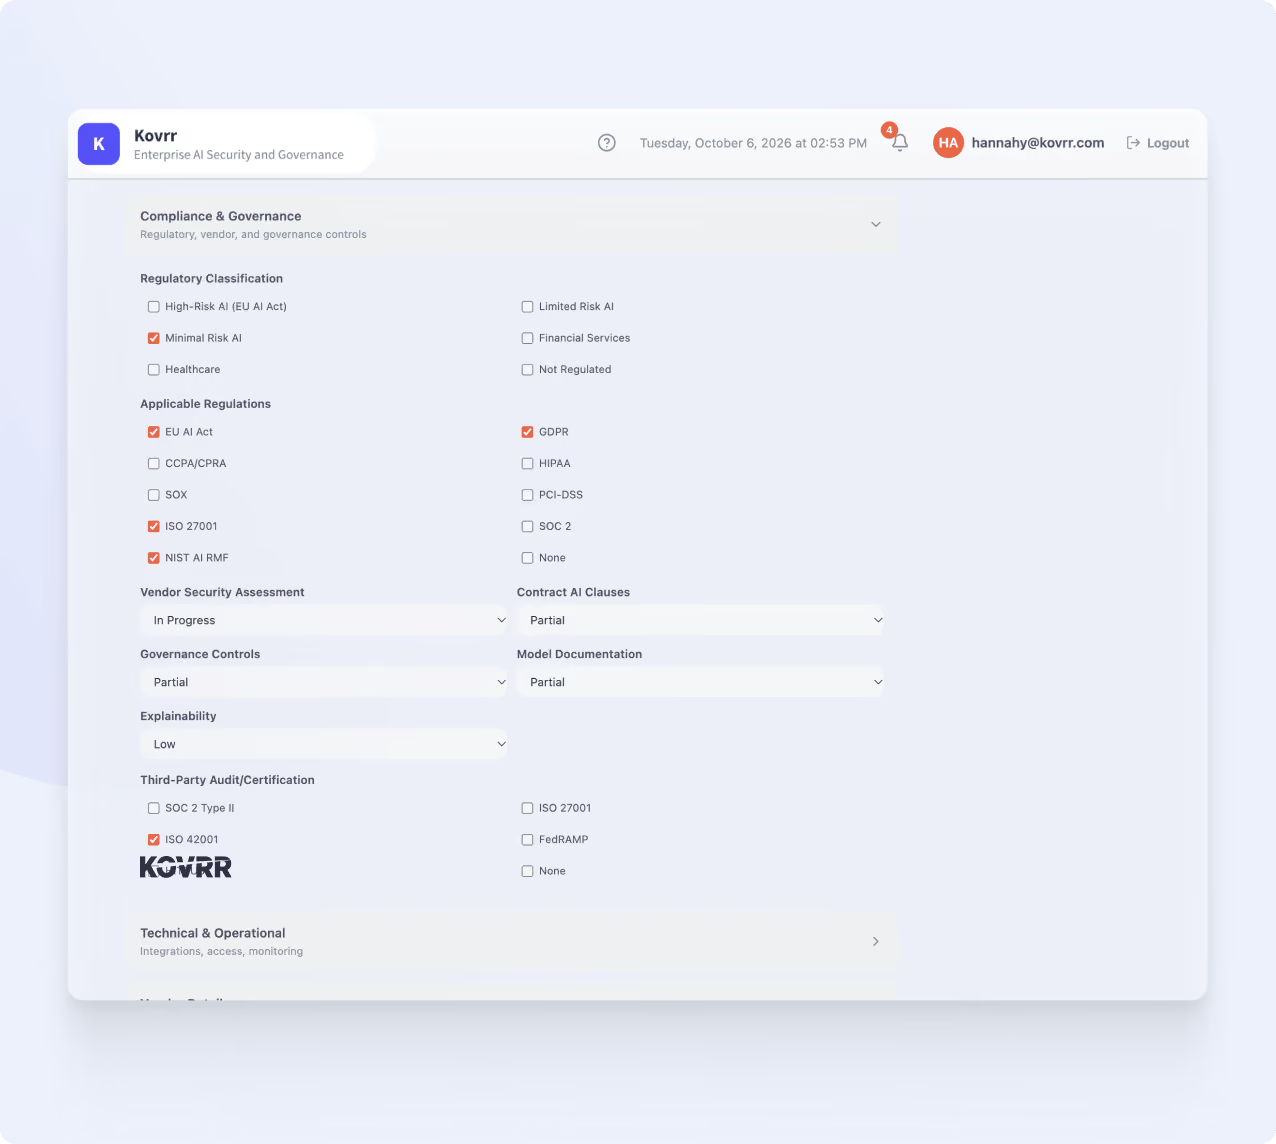
The platform allows you to benchmark vendor maturity against recognized frameworks such as NIST AI RMF and ISO 42001, giving risk and compliance teams the structure to monitor adherence and accountability.
Assess vendor safeguards and governance controls against frameworks and regulations.
Review AI vendor risk profiles showing compliance posture, incidents, and stability indicators.
Document certifications, policy misalignments, and data governance gaps within a single dashboard.
Track improvement progress and contract updates through ongoing assessments and renewal monitoring.
These insights not only support due diligence but also provide structured inputs for modeling vendor-driven financial exposure.
Explore the AI Vendor Risk Catalog
Access Kovrr’s AI Vendor Risk Catalog to review structured intelligence on AI providers, understand third-party AI risk considerations, and strengthen oversight across your extended supply chain. Use it to inform due diligence, benchmark vendors, and support defensible AI third-party risk management decisions.


Monitor Changes as Your Vendor Ecosystem Evolves
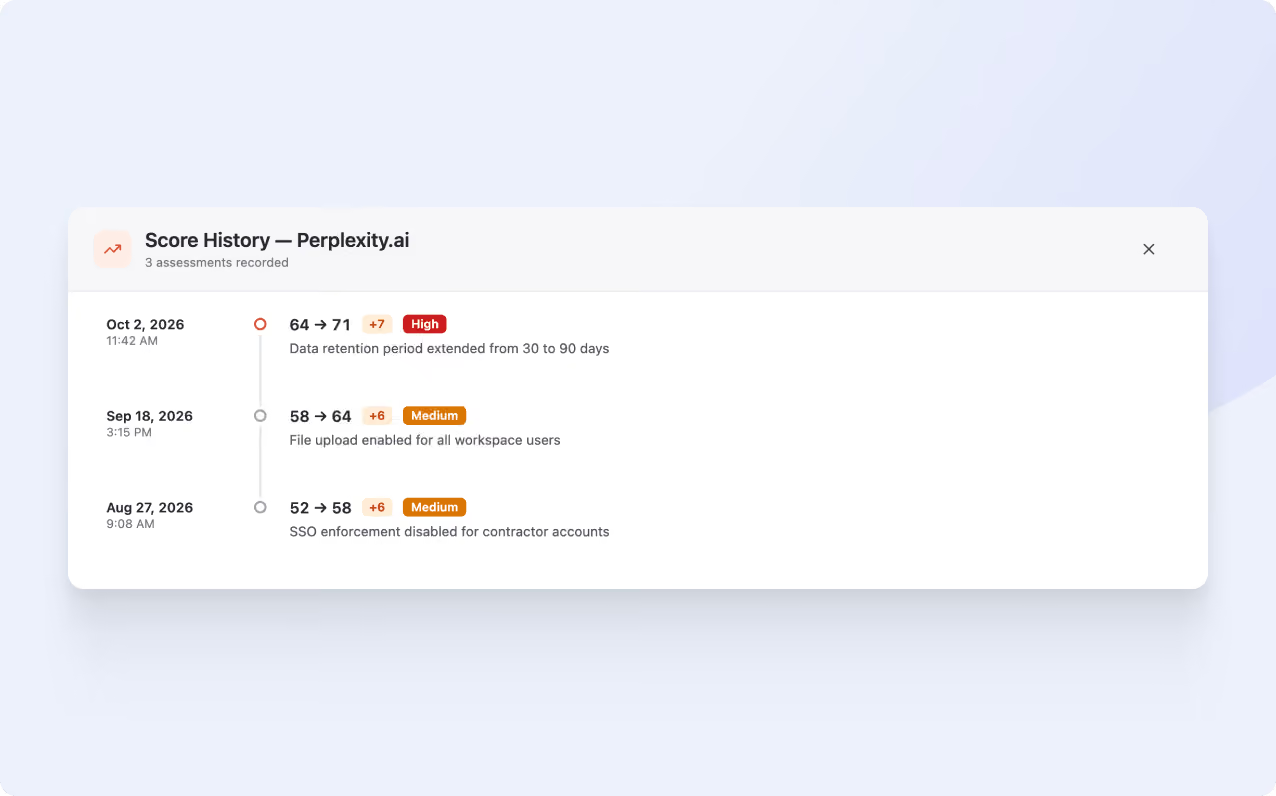
Vendors update models, expand capabilities, or integrate new AI tools that alter their risk profiles. Kovrr automatically detects these changes, updating each vendor’s risk signals, compliance status, and contract data in real time. Continuous monitoring ensures oversight remains accurate as the supply chain evolves, reducing the gap between vendor change and organizational awareness while maintaining up-to-date financial exposure data for risk modeling.
Why Third-Party AI Risk Management Matters
Third-party providers often operate outside direct oversight, yet their AI-driven systems still process sensitive data and influence critical workflows. Kovrr’s AI third-party risk management platform closes that gap with continuous monitoring and compliance benchmarking, giving leaders a verified view of external AI exposure. When integrated with AI Risk Quantification (AIRQ), these insights translate into modeled financial impact, enabling organizations to prioritize oversight efforts based on defensible, data-driven risk analysis.
Quantify Third-Party
AI Exposure
Kovrr’s AI Risk Quantification (AIRQ) engine models how vendor-driven AI and agentic AI exposure translates into projected financial impact. By integrating third-party monitoring data into quantification models, organizations gain a defensible basis for prioritizing supplier oversight and mitigating systemic AI risk.
AI Third-Party Risk Management FAQs
Schedule a DemoWhat is AI third-party risk management?

What types of AI vendors or partners can be evaluated with this platform?
How often should organizations review third-party AI governance maturity?
Does the third-party AI risk management platform support AI Risk Quantification (AIRQ)?
