Blog Post
The Cyber Loss Where the Stolen Records Belong to Other Companies
September 30, 2026
A breach response begins with a record count and a notification assessment. How many individuals, in which jurisdictions, under which statute.
Some organizations hold almost no personal data and enormous quantities of other companies' commercial confidences. An insurer's claims files contain policyholders' loss histories, control failures and settlement amounts. The statutory machinery may not engage at all, and what engages instead is a contract portfolio.
Does Notification Law Apply?
Frequently not, which is the first thing to establish because the whole prepared playbook depends on it.
Breach notification obligations across the United States and in Europe are keyed to personal information and often only apply to personal data. A file describing another company's loss experience, its control weaknesses and what it settled for contains no natural person's data in many cases, so no statutory duty to notify anybody attaches.
Which Removes the Familiar Structure
No regulator to notify, no individuals to write to, no credit monitoring to offer, and no statutory deadline. An incident response plan built entirely around those steps has nothing to execute, and the absence of a legal deadline is not an absence of obligation.
Is a Breach a Breach of Confidentiality?
Not automatically, and the distinction is more favorable to the holder than most people assume.
Courts have held that a duty not to disclose is not a duty to secure. A confidentiality clause typically obliges the receiving party not to disclose, and an attacker taking data is not the holder disclosing it. So a standard confidentiality provision may not be breached by an exfiltration at all.
The Definitions Do Not Line Up
Confidentiality clauses frequently define confidential information narrowly, covering material that was labeled as such or that a reasonable person would treat as confidential. The contractual definition and the scope of data protection law overlap partially rather than fully, so some exposed data is regulated and not contractually confidential while other exposed data is the reverse.
Where Does the Exposure Sit Instead?
In security representations rather than confidentiality clauses, which is the finding worth acting on.
Statements about how data will be protected, frequently drafted outside legal, can support an implied contract claim following an incident. One court declined to dismiss such a claim where the defendant's own published representations about its security practices were relied on. So the liability follows what you said you would do rather than what you promised not to do.
The Inventory Is an Unusual One
The relevant documents are the security addendum, the questionnaire responses given during procurement, the certifications cited in a proposal and the security claims on a website. Each is a representation somebody may have relied on, and none of them lives with the contract, which the difference between an attestation and evidence covers from the other direction.
What Makes the Loss Computable?
Liquidated damages clauses, which appear precisely because this kind of harm resists calculation.

Courts enforce a preset damages figure where the amount is reasonable and where damages would be difficult to establish. Commercial confidence damages are exactly that, so these clauses are both more likely to appear in this kind of agreement and more likely to be upheld. The sum across the portfolio is a computable exposure.
Which Gives Two Terms
The liquidated sum where clauses exist, and an argued figure where they do not. The second is the harder one and it is also the one a counterparty struggles to prove, so the presence of a liquidated clause cuts both ways rather than simply increasing exposure.
What Is the Counterparty's Own Loss?
Potentially permanent, and that permanence is what drives a claim.
Where the exposed material was protectable as a trade secret for the counterparty, publication can end that protection irreversibly. A pricing model, a claims strategy or an admission about a control weakness is not restored by anything the holder does afterward. So the counterparty has an unrecoverable loss and a contract to pursue it under.
Which Category Is Most Damaging?
Admissions rather than figures. A settlement amount is commercially awkward, and a documented acknowledgment that a control failed is usable against the counterparty by its own adversaries, regulators and counterparties. The holder is exposing somebody else's worst internal statement about itself.
When Does the Clock Start?
Whenever each contract says, and those deadlines are frequently shorter than any statutory one.
Contractual notification windows commonly run to twenty-four or forty-eight hours, tighter than the seventy-two hours a European controller has, because a counterparty needs time to meet its own obligations after being told. So an organization with no statutory deadline may have dozens of contractual ones, each running from a different definition of awareness.
The Response Is a Contract Exercise
The first task is establishing which counterparties' data was affected and what each agreement requires, rather than counting records. The task is a legal and commercial exercise conducted at speed, and it needs the contract terms indexed before an incident rather than retrieved during one, and producing anything on somebody else's timeline is the capability being tested.
Does Cyber Insurance Respond?
Partly, and the boundary follows the same line as the notification analysis.
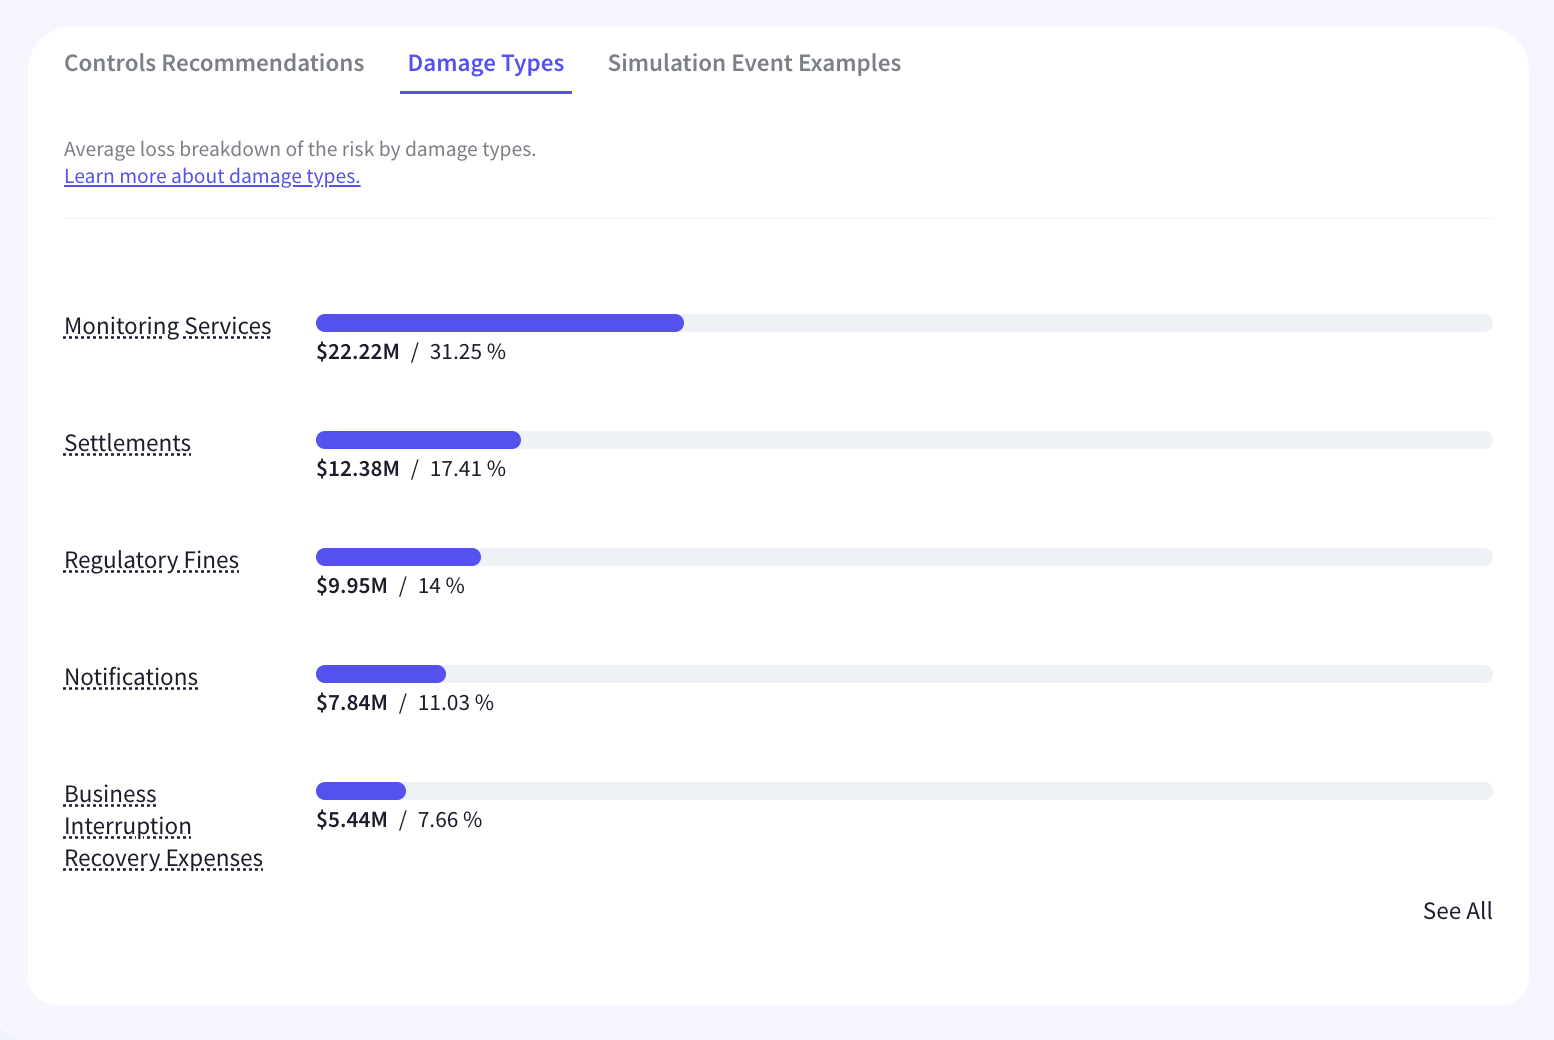
Cover is generally built around privacy liability and the costs of a personal data breach, covering notification, monitoring, regulatory defense and related response. A claim from a corporate counterparty for breach of contract or breach of confidence is a different insuring agreement, and whether it responds depends on whether the policy carries network security liability or contractual liability wording broad enough to reach it.
Which Exclusion Matters Most Here?
Contractual liability, since many policies exclude liability assumed under contract that would not exist at law. A liquidated damages clause is liability assumed under contract almost by definition, so the most computable part of the exposure may be the least insured part of it, and the terms that surface at claim is where that gets discovered otherwise.
What Should Be Asked at Renewal?
Whether the policy responds to a claim by a corporate counterparty where no personal data was involved. The question separates a program built for a consumer-facing breach from one built for this exposure, and the answer is frequently that it does not.
What Should Be Established?
Four things, and all four sit with legal rather than with security.
The sum of liquidated damages clauses across agreements covering confidential material. How many agreements contain security representations rather than only confidentiality undertakings, since that is where implied contract exposure lives. The shortest contractual notification window in the portfolio, because it sets the response clock. Then which counterparties' material would be identifiable if exposed, since unattributable data produces a smaller claim. Cyber risk quantification built on those inputs produces a figure a per-record model cannot reach.
Count Contracts, Not Records
Breach notification law is keyed to personal information, so an organization holding other companies' commercial confidences may have no statutory duty and no prepared response that applies. A confidentiality clause may not be breached either, since courts have held that a duty not to disclose is not a duty to secure and an attacker taking data is not the holder disclosing it. The exposure sits instead in security representations, which are frequently drafted outside legal and can support an implied contract claim. Liquidated damages clauses make part of it computable, and they appear here because this harm resists calculation. The counterparty's loss may be permanent where trade secret protection ends, and the most damaging category is a documented admission rather than a figure. Kovrr's cyber risk quantification models the contract portfolio as the exposure.
To see exposure modeled from contractual terms rather than from a per-record cost, book a demo with our risk experts.
Commercial Confidence Exposure FAQs
Speak to an ExpertDoes breach notification law apply to business data?

Is a data breach automatically a breach of confidentiality?
Where does the liability sit if not in the confidentiality clause?
What are liquidated damages for a confidentiality breach?
Can a contractual breach notification deadline be shorter than GDPR?
What is the most damaging category of exposed commercial data?