Blog Post
Losing the Right to Process
September 20, 2026
A regulatory penalty arrives from a regulator, through a published process, with stated periods and a route of appeal. The payment card standard works differently in every one of those respects, and the difference is the whole exposure.
The body that writes the standard does not enforce it. Enforcement runs through the card networks to the acquiring bank and then to the merchant under a commercial contract, which changes the timeline, the discretion available and who there is to negotiate with.
What Is Being Breached?
A contract rather than a standard, which is the structural fact everything else follows from.
Each card network publishes its own operating rules governing participation in its system, and those rules reference the security standard as the underlying requirement. A merchant accepted those rules when its acquirer signed it up to accept cards. So a merchant failing the standard is in breach of the network's operating rules through its acquirer agreement rather than in violation of a law.
The Remedy Is Commercial
A statutory penalty is applied by an authority with defined powers. A contractual remedy is applied by a counterparty with commercial discretion, and discretion cuts in both directions. The same non-compliance can produce different outcomes for two merchants depending on the value of the relationship, which is the opposite of how regulatory enforcement is supposed to work.
Who Pays and in What Order?
The chain has three links and the merchant sits at the end of it.

The network assesses the acquiring bank, since the bank is the party contractually accountable for its merchants' compliance. The acquirer then passes the cost through under the merchant agreement, which is where the clause permitting it lives. The merchant pays and the intermediary is a conduit.
Why Does the Indirection Matter?
Because the merchant has no relationship with the party setting the amount. Questions about how a figure was arrived at go to an acquirer that received it rather than to the network that determined it, and the merchant's leverage is over its acquirer relationship rather than over the assessment.
What Do the Published Figures Tell You?
Less than they appear to, and this is worth being careful about because the numbers circulate as though they were official.
Monthly non-compliance fees are widely reported starting in the low thousands and escalating into the tens of thousands as a lapse persists, with larger figures for higher-volume merchants. Every source describing those ranges characterizes them as industry averages rather than published schedules, because the networks do not publish a penalty table and the amounts are set within a commercial relationship.
Where Is the Authoritative Figure?
The merchant agreement, which states what the acquirer may pass through and on what terms. An organization modeling this exposure from published averages is modeling somebody else's contract, and reading its own is a shorter exercise with a better answer.
Where Is the Real Tail?
Not in the fees, which is the reason a model built on them understates the shape badly.
Persistent non-compliance or a serious breach can result in the acquirer terminating the merchant account, which removes the ability to accept card payments immediately. For most merchants that is not a penalty, it is the end of trading in its current form, and it arrives through a commercial decision rather than an enforcement action.
The Consequence Outlasts the Incident
A terminated merchant can be added to an industry listing that other acquirers consult, which makes obtaining processing elsewhere difficult for years afterward. So the tail is not a large fine, it is a multi-year impairment of the ability to transact, and interruption rather than data loss is the closer analogue than a penalty scenario.
How Many Bills Arrive From One Event?
Several, from different parties, which is why a single-figure estimate misses most of it.
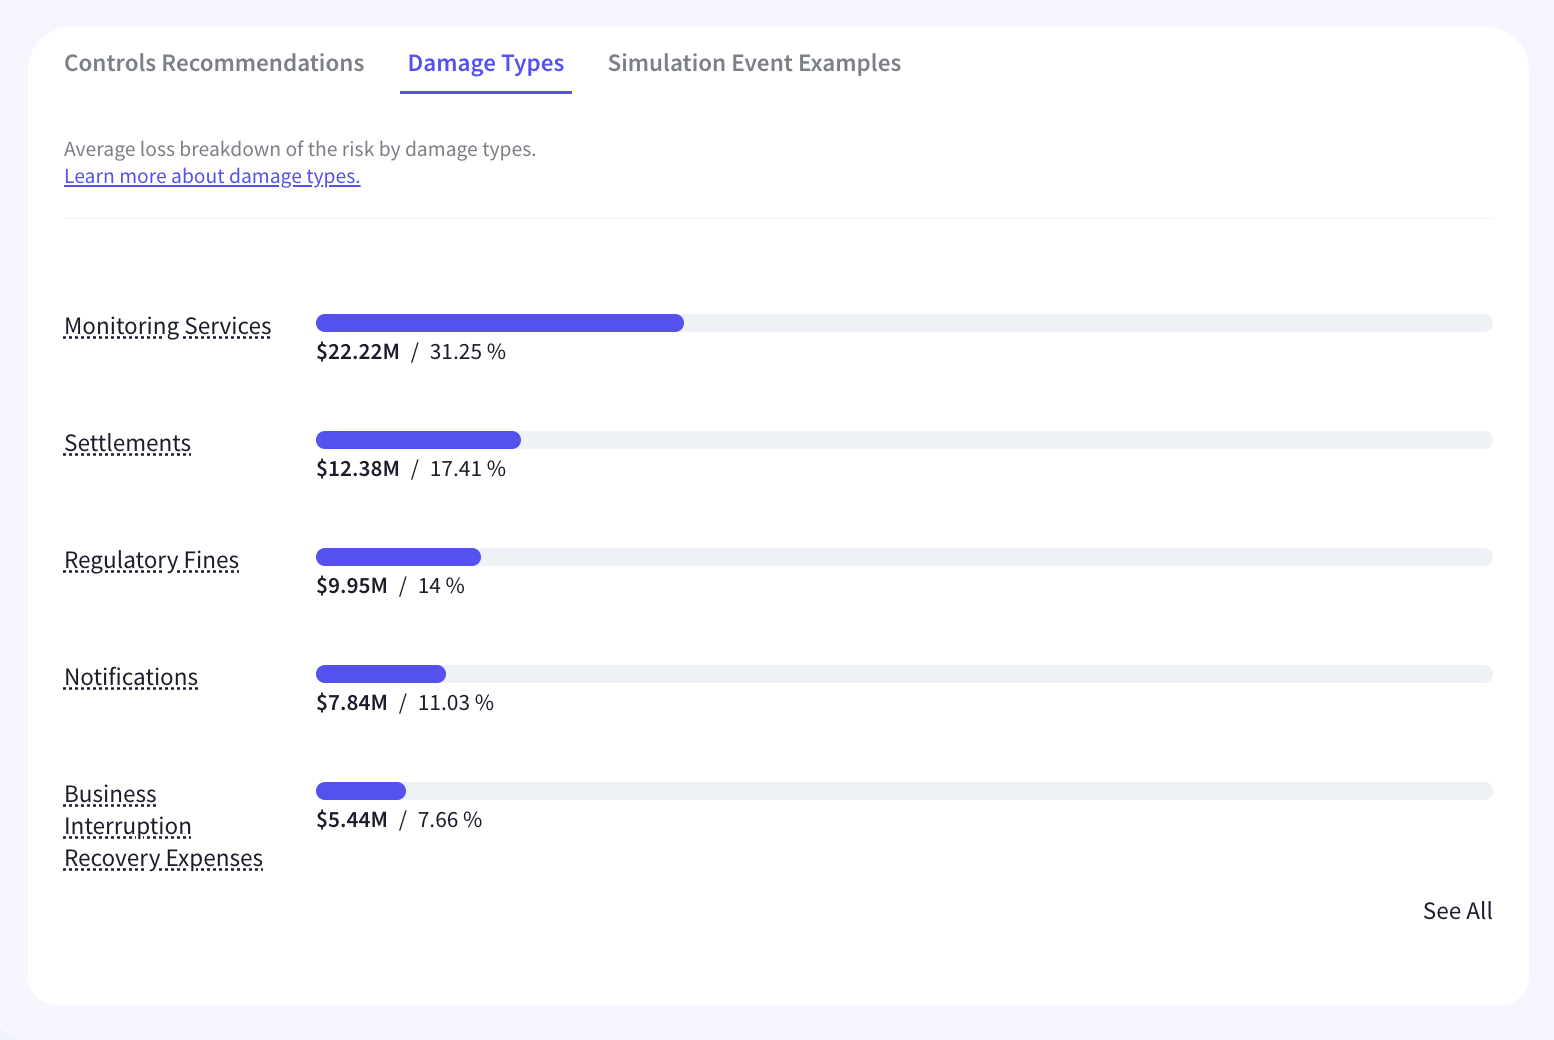
A suspected compromise triggers a mandated forensic investigation the merchant funds. Card reissuance is charged per card. Fraud losses on compromised accounts may be recovered through the chain. Non-compliance fees run monthly while the position is unresolved. Transaction pricing can also be increased for the duration, which is a recurring cost rather than a one-off.
Which Component Is Most Often Omitted?
The pricing increase, because it does not arrive as a bill. An elevated rate applied across every transaction for a year is a substantial figure that appears in cost of sales rather than in an incident ledger, so nobody adds it to the loss, and separating the components of a loss figure is what keeps it visible.
Does a Breach Require Non-Compliance?
No, and the asymmetry is worth understanding before relying on a compliance certificate.
Assessments can follow a breach whether or not a validation lapse is established, since the investigation examines the position at the time of the compromise rather than the paperwork. A merchant holding a current validation can still be found non-compliant retrospectively on the specifics of what happened, so the certificate evidences a point in time rather than a state.
Which Argues for Continuous Rather Than Annual Validation
An annual assessment establishes the position on one date. The exposure depends on the position during whatever window a compromise occurred in, and those coincide rarely, which what annual testing misses covers directly.
Which Merchants Carry the Most Exposure?
Not the largest, which is counterintuitive and follows from where the leverage sits.
A high-volume merchant is valuable to its acquirer, has a negotiated agreement, and would be expensive to lose. The relationship produces tolerance during a remediation period and a commercial conversation rather than an immediate escalation. A small merchant on standard terms has none of those, so the same lapse can move faster toward the outcomes that matter.
Which Inverts the Usual Severity Assumption
Loss models generally scale severity with size, since a larger organization has more revenue at risk. Here the probability of reaching the tail runs the other way, because termination is a commercial decision and a small account is easier to terminate. Large merchants face a bigger number and a smaller chance of it, and the two effects partly offset.
What Does That Mean for a Smaller Organization?
The tail deserves more weight than its revenue suggests, and that the mitigation is relationship rather than technical. Knowing whether an alternative acquirer would accept you, before you need one, is the control that addresses the tail directly, and dependency you cannot diversify away is what a single acquirer relationship is.
What Should Be Established?
Four things, and the first is a document nobody in security usually reads.
What the merchant agreement says about pass-through of network assessments, remediation deadlines and termination rights, since that is the exposure that applies. What proportion of revenue depends on card acceptance, which sets the severity of the tail. Whether an alternative acquirer relationship exists or could be established quickly. Then what the validation cadence is against how long a control lapse might go unnoticed. Cyber risk quantification built on the contract rather than on published averages produces the figure that applies to you.
Read the Contract, Not the Standard
The body that writes the payment card standard does not enforce it. The networks assess the acquiring bank, the acquirer passes the cost through under the merchant agreement, and the merchant pays without any relationship to the party that set the amount. The remedy is contractual rather than statutory, so discretion applies and two merchants in the same position can be treated differently. The widely circulated fee ranges are industry averages rather than published schedules, and the authoritative figure sits in your own agreement. The tail is also not a fine at all, since termination removes the ability to transact and an industry listing can impair obtaining processing elsewhere for years. Kovrr's cyber risk quantification models that as an interruption scenario rather than a penalty one.
To see card acceptance exposure modeled as an interruption scenario with its tail priced, book a demo with our risk experts.
Payment Compliance Exposure FAQs
Speak to an ExpertWhat is breached in a payment compliance failure?

Why does the contractual route change the exposure?
Who pays and in what order?
How reliable are the published fine figures?
Where is the real tail of this exposure?
Can assessments follow a breach even where validation was current?