NIST CSF 2.0
NIST Cybersecurity Framework 2.0 is the second major version of the NIST Cybersecurity Framework, published in 2024, adding the Govern function and expanding the framework's scope beyond critical infrastructure to organizations of any type and size.
How NIST CSF 2.0 Is Structured
CSF 2.0 organizes cybersecurity outcomes around six functions: Govern (the new addition), Identify, Protect, Detect, Respond, and Recover. Each function contains categories, which in turn contain subcategories describing specific outcomes.
The framework is outcome-focused rather than control-focused. It describes what should be true (assets are managed, threats are detected, incidents are contained) without prescribing exactly which controls to implement. Organizations pair CSF with control catalogs like NIST 800-53 or CIS Controls for implementation detail.
Why the Govern Function Was Added
CSF 1.1 covered operational cybersecurity outcomes. It did not explicitly address the governance layer underneath them: leadership commitment, policy, roles, oversight of third parties, and integration with enterprise risk management. Practitioners increasingly treated governance as implicit but essential.
CSF 2.0 made it explicit. The Govern function now sits alongside the operational functions, applying continuously across all of them.
Why NIST CSF 2.0 Matters
CSF is one of the most widely adopted cybersecurity frameworks globally. Boards, regulators, cyber insurers, and enterprise buyers routinely reference it. CSF 2.0's elevation of governance mirrors similar changes in the NIST AI RMF and broader regulatory direction, and reflects the sector-wide view that governance is foundational rather than optional.
NIST CSF 2.0 and Quantification
CSF is framework-neutral on how outcomes are measured. Programs increasingly overlay CRQ on CSF-structured outcomes, so a program can describe both its qualitative maturity (CSF Tier or Profile) and its quantified exposure (dollars-based CRQ outputs).
How Kovrr Approaches NIST CSF 2.0
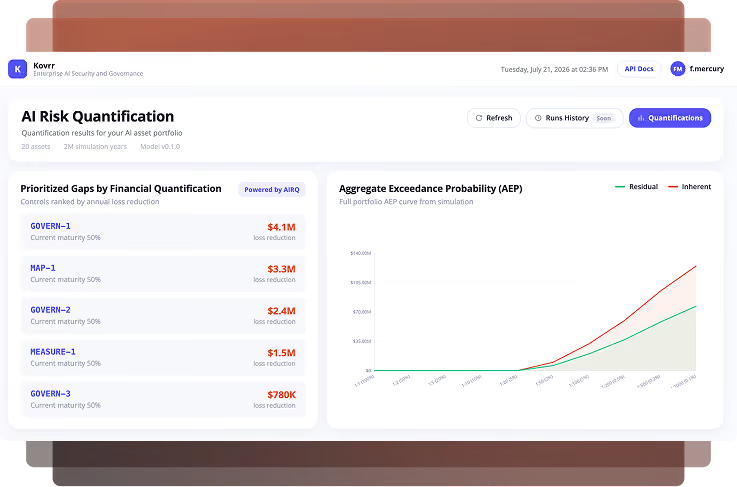
Kovrr's Cybersecurity GRC capability maps controls and quantified exposure against CSF 2.0 functions, categories, and subcategories, so programs can report against CSF while also producing financial exposure for board and CFO conversations.
Related Terms


Turn Cyber Risk Into Financial Exposure the Board Can Act On
Security leaders are being asked to defend budgets, prioritize controls, and report cyber risk in the same terms as every other enterprise risk. Kovrr's CRQ Platform models loss scenarios, benchmarks control performance, and gives the C-suite a defensible view of where cyber sits on the balance sheet.