Risk Register
A risk register is the documented catalog of identified risks, their assessment (likelihood, impact, or quantified exposure), treatment status, ownership, and monitoring information, serving as the operational backbone of enterprise risk management.
What a Risk Register Contains
Standard entries in a risk register include a risk description, categorization (typically by risk type, business unit, or process), assessment data (likelihood and impact, or quantified exposure), treatment approach and status, owner, and review cadence. Cyber-specific registers may add threat category, affected assets, control mappings, and scenario references.
The register is not just a list. It is a working artifact used for prioritization, escalation, treatment tracking, and reporting.
Cyber Risk Register Specifics
Cyber risk registers typically differ from broader enterprise registers in a few ways. They are updated more frequently because cyber exposure changes faster. They reference specific technical scenarios and controls. They increasingly express exposure quantitatively rather than through qualitative ratings.
See Kovrr's Cyber Risk Register.
Registers and CRQ
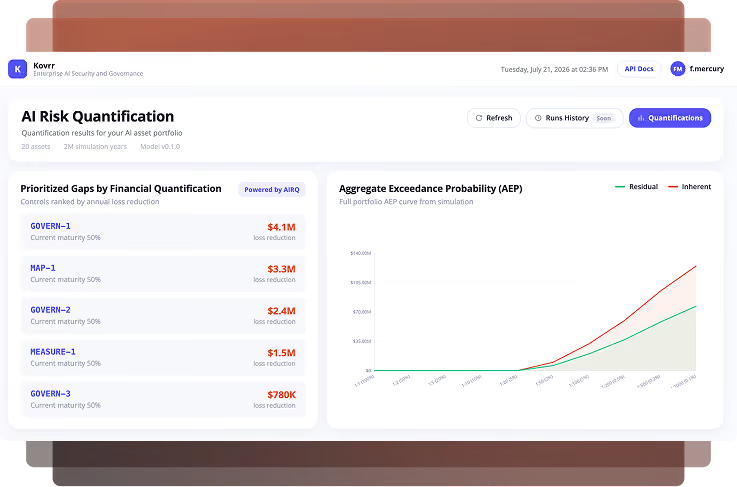
Traditional registers ranked risks by qualitative severity scores. Modern registers driven by CRQ rank by quantified exposure, so prioritization is defensible in financial terms and directly comparable across risk categories.
How Kovrr Approaches the Cyber Risk Register
Kovrr's Cyber Risk Register capability builds the register directly on CRQ outputs, so risks are quantified, prioritized in dollar terms, and connected to the specific scenarios and controls driving them.
Related Terms


Turn Cyber Risk Into Financial Exposure the Board Can Act On
Security leaders are being asked to defend budgets, prioritize controls, and report cyber risk in the same terms as every other enterprise risk. Kovrr's CRQ Platform models loss scenarios, benchmarks control performance, and gives the C-suite a defensible view of where cyber sits on the balance sheet.