Blog Post
When the Penalty Accrues Every Day It Goes Unnoticed
September 17, 2026
Cyber loss models place the loss at the incident. Something is attacked, something is lost, and the cost follows from what was taken and how long systems were down.
An electric utility carries a loss category that does not work that way. Reliability standards carry penalties assessed per violation and per day, so the cost accrues from the moment a non-compliant condition begins rather than from the moment anything happens to it. The loss event is an audit rather than an attack.
Why Does Per-Day Assessment Change the Model?
Because duration becomes a multiplier on the count rather than a separate term, and the duration runs backward from discovery rather than forward from an incident.
A conventional regulatory penalty is a single amount assessed once. A per-violation per-day structure means a misconfiguration present across forty assets for two years is forty violations multiplied by seven hundred and thirty days. The statutory maximum sits above one and a half million dollars per violation per day after inflation adjustment, which makes the arithmetic large quickly even though settled penalties land far below the ceiling.
The Exposure Is Already Accruing
Nothing has to happen for the figure to grow. A condition nobody has noticed is adding to the count every day it persists, so the exposure at any moment is a function of how long the organization has been in a state it has not yet discovered. The relationship differs from every other cyber loss category.
What Does the Enforcement Record Show?
The large figures come from accumulation rather than from severity, which is the pattern worth modeling.

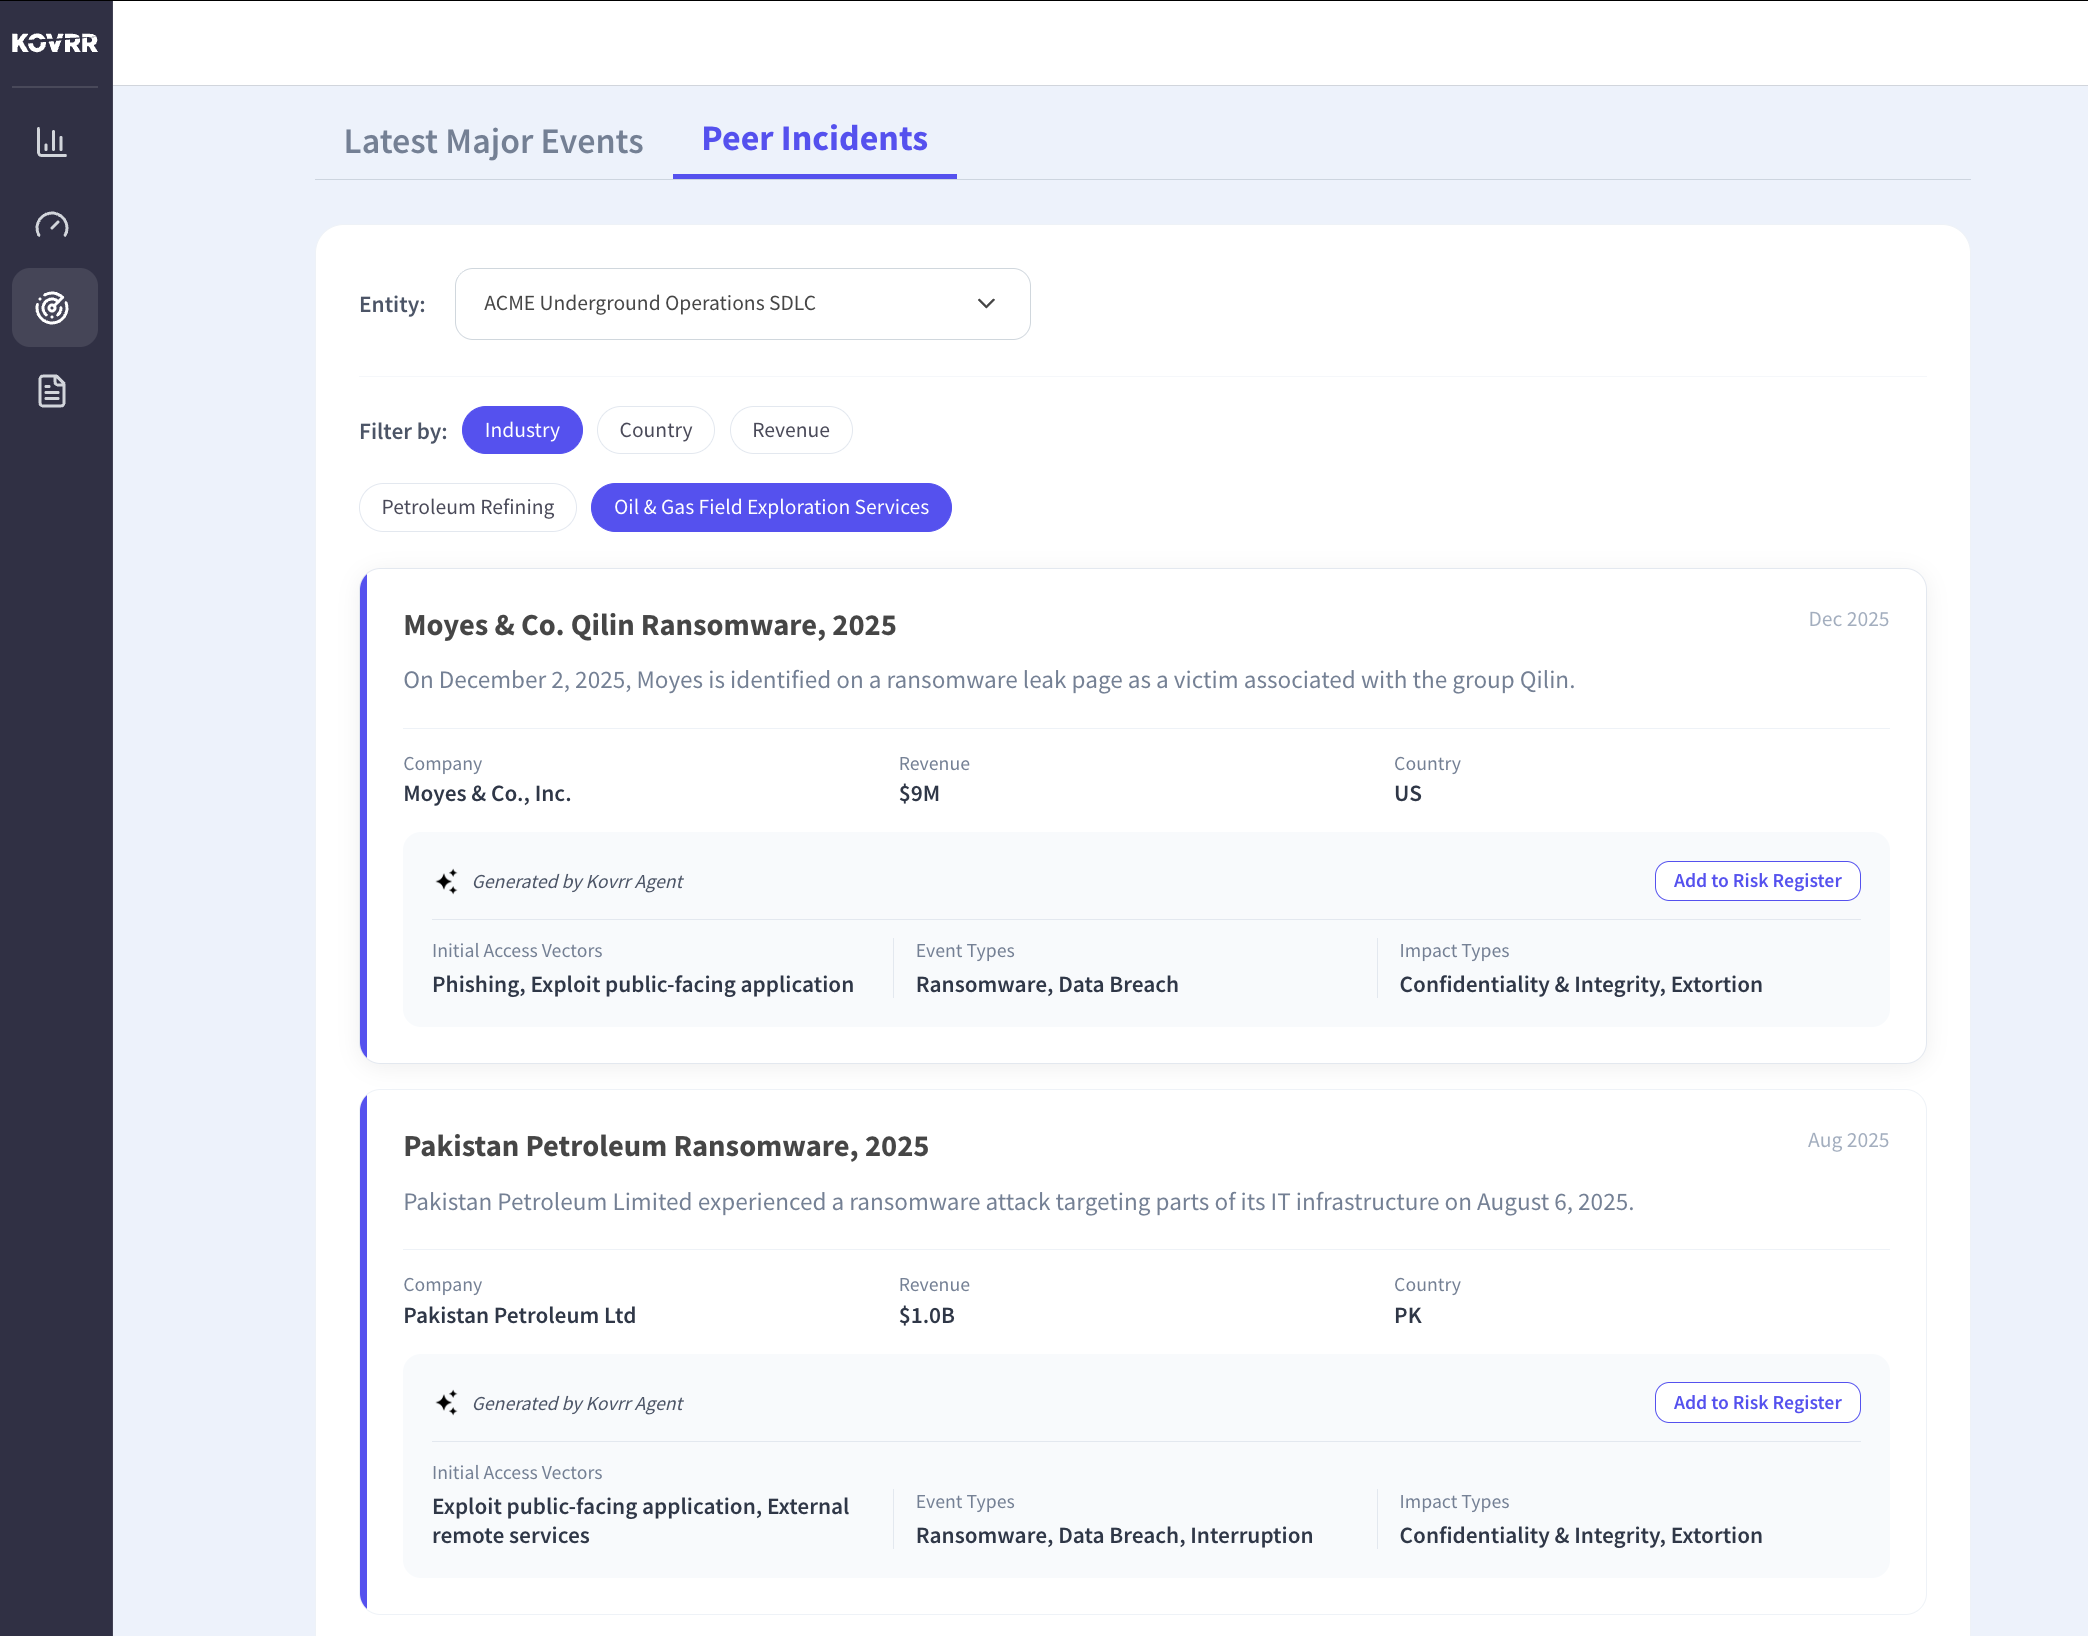
The largest publicly reported action in this regime reached ten million dollars and covered a hundred and twenty-seven separate violations built up across several years. No single failure produced it. Sustained conditions across multiple standards surfaced together during a formal audit, and the total reflected count multiplied by duration rather than the consequence of any event.
Which Findings Recur?
Asset categorization, baseline configuration records, change management against those baselines, evidence of access management and incident response documentation. Every one is a record-keeping condition rather than a technical weakness, which is why they persist unnoticed and why the common position is partial compliance rather than deliberate non-compliance.
Why Is Self-Discovery Worth Something?
Because self-reporting typically attracts a lower penalty than a condition found by an auditor, which turns discovery into a decision with quantifiable value.
An organization that finds a condition, reports it and mitigates is in a materially better position than one where the same condition surfaces during an audit. So investment in continuous verification has a return that most control investments lack, since it reduces the penalty on conditions that already exist rather than only preventing new ones.
How Would You Price That?
As the difference between the two treatments applied to the conditions you probably have but have not found. Estimating undiscovered non-compliance sounds impossible and is approximable from the rate at which your last few audits or self-assessments surfaced conditions nobody knew about, and continuous verification against periodic testing is the investment being priced.
What Does the Mitigation Plan Cost?
Frequently more than the penalty, which is the part organizations discover after the financial figure has been absorbed.
An enforcement finding requires a documented plan identifying root cause, corrective actions, a milestone schedule and demonstrated completion, and the plan is itself audited for effectiveness. The engineering and documentation effort to satisfy that across a distributed asset base consumes people who would otherwise be operating the system, and the cost lands over quarters rather than at once.
Which Belongs in the Model as a Separate Term
Penalty and remediation are different quantities with different timing, so a single figure conceals which one dominates. Where remediation exceeds the penalty, the case for finding conditions early is stronger than the penalty arithmetic alone suggests, and pricing a weakness while it stays open is the same reasoning applied to a security control.
Is Any of This Insured?
Largely not, which is worth establishing before the exposure is presented as manageable.
Regulatory penalties are commonly excluded or narrowly covered, and policies may exclude penalties arising from willful violations specifically. Insurers in this sector also frequently require evidence of compliance as a condition of cover, so the compliance position affects whether the rest of the program responds rather than only whether penalties are paid. The exposure is therefore closer to retained than to transferred.
What Does That Mean for the Investment Case?
The usual comparison does not apply. A retained exposure accruing daily, with a remediation cost exceeding the penalty and a discount available for finding it yourself, produces a stronger funding case than a transferable one of the same size, and cyber risk quantification that separates retained from transferred exposure is what shows it.
Where Does the Service Interruption Loss Sit?
Alongside this rather than instead of it, and the two are frequently conflated in a single figure.
An outage affecting supply carries its own consequences, including recovery cost, regulatory reporting on separate timetables and in some cases direct customer compensation. What it does not carry is revenue loss in the ordinary sense, since a regulated utility recovers cost through a rate structure rather than through sales that stop, which the substitution where revenue is not the denominator covers.
Which Loss Is Larger?
Usually the compliance one, which is counterintuitive and follows from the arithmetic. An outage is bounded by its duration in hours or days. An accumulated compliance condition is bounded by how long it went undiscovered, measured in years, multiplied by an asset count. The dramatic scenario is smaller than the quiet one.
How Do You Estimate the Frequency?
Not as a frequency at all, which is the departure from a conventional model and the reason this scenario resists the usual treatment.
An attack has a rate. A compliance audit has a schedule, since audits occur on a known cycle whether or not anything is wrong. So the probability of the loss event is close to one over the audit period, and the uncertainty sits entirely in what the audit finds rather than in whether it happens.
Which Changes What the Model Produces
A distribution over findings rather than over events. The useful question is how many conditions exist, how long each has persisted and how many an audit surfaces, all of which are estimable from the organization's own history. The output is a loss given audit with a stated range, which is more defensible than an annualized figure derived from a frequency that is really a calendar.
Does That Make It Easier or Harder to Model?
Easier, and it is one of the few cyber-adjacent exposures where that is true. The event is scheduled, the penalty structure is published, the enforcement record is public and the conditions are internally discoverable, which peer benchmarking supports better here than in most scenarios. Compared with estimating the rate of a novel attack, this is a well-specified problem, and working without an incident history is harder than working with a known audit cycle.
What Should Be Established First?
Three things, and the first is the one that sizes everything else.
How long the organization would take to discover a non-compliant condition that arose today, since the interval is the multiplier. What the last two audits or self-assessments surfaced that nobody knew about, which indicates the rate of undiscovered conditions. Then whether remediation capacity exists to execute a mitigation plan without stopping other work, since that determines the second cost term. Where a compliance program breaks down is usually in the evidence rather than in the control.
The Loss Event Is the Audit
Reliability penalties assessed per violation and per day put duration inside the count rather than beside it, and the duration runs backward from discovery rather than forward from an incident. So the exposure accrues while nothing happens, and the largest recorded actions came from sustained record-keeping conditions surfacing together rather than from any single failure. Self-discovery attracts lower treatment than auditor discovery, which gives continuous verification a return most control investments lack. The mandated remediation frequently costs more than the penalty. Regulatory penalties are also largely uninsured, so this is retained exposure rather than transferred. Kovrr's cyber risk quantification separates the two and prices the interval before discovery.
To see compliance and interruption exposure modeled separately for a regulated utility, book a demo with our risk experts.
Utility Compliance Exposure FAQs
Speak to an ExpertWhy does per-day penalty assessment change the loss model?

What does the enforcement record show?
Which compliance findings recur?
Why is self-discovery worth something?
What does the mitigation plan cost?
Is regulatory penalty exposure insured?