AI Coding Agent Security
AI coding agent security is the practice of governing AI assistants that read source code, execute commands and submit changes, covering the credentials they hold and the code they produce.
Coding Agents Hold More Than Source Code
An agent with repository access reaches the configuration files, infrastructure definitions and committed secrets that live alongside the code. Running on a developer's machine, it also inherits that machine's cloud credentials and internal network position. The permission set is wide because development machines are wide, and nobody provisioned the agent deliberately.
Execution Is the Point and the Exposure
A coding assistant earns its value by running tests, installing dependencies and executing scripts. Every one of those capabilities is also what makes a manipulated instruction consequential. A dependency pulled during a build, a README in a cloned repository or a comment in an issue can carry indirect prompt injection into an agent holding a shell. Containment through an agent sandbox is the control that matches this exposure.
Generated Code Arrives Without Provenance
Code an agent writes carries no marker distinguishing it from human work once it is committed. Vulnerability patterns reproduced from training data enter the codebase, licensed fragments arrive with no attribution, and review processes calibrated for human output meet volume they were not sized for. Recording which changes an agent authored is what makes a later audit possible.
The Governance Problem Is Positional
Most of this happens on laptops, through local processes and local MCP servers, with nothing crossing the network in a form that network telemetry reads. Kovrr's work on governing AI coding agents on developer laptops covers why endpoint position is required here. The same machines are where shadow MCP servers appear, which makes them a single surface rather than two separate problems.
Related Terms

Full AI Visibility. Full Control. One Connected Platform.
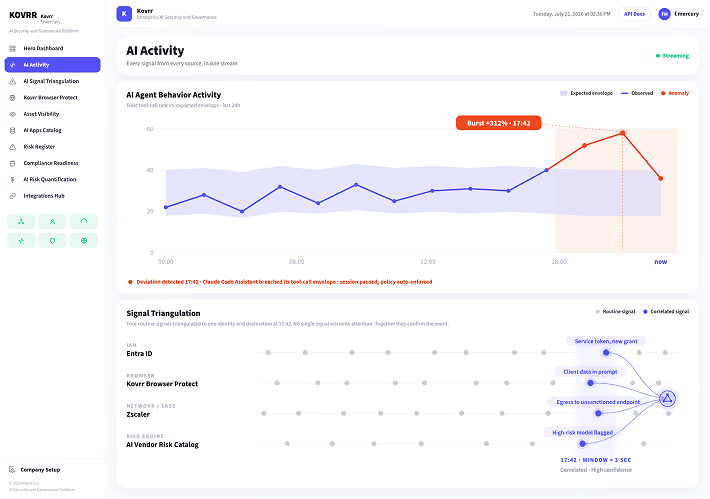
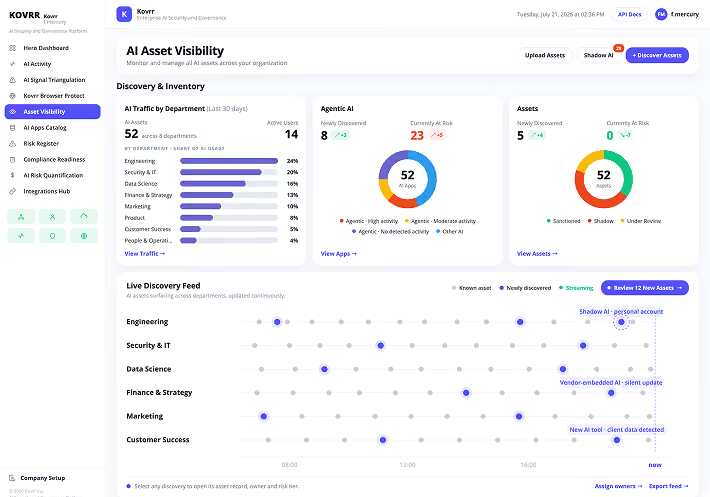
Enterprise AI is expanding faster than most governance programs can track. Kovrr connects every AI signal across browser, endpoint, network, identity, and vendor systems into a single platform so security, governance, and risk teams work from the same evidence.