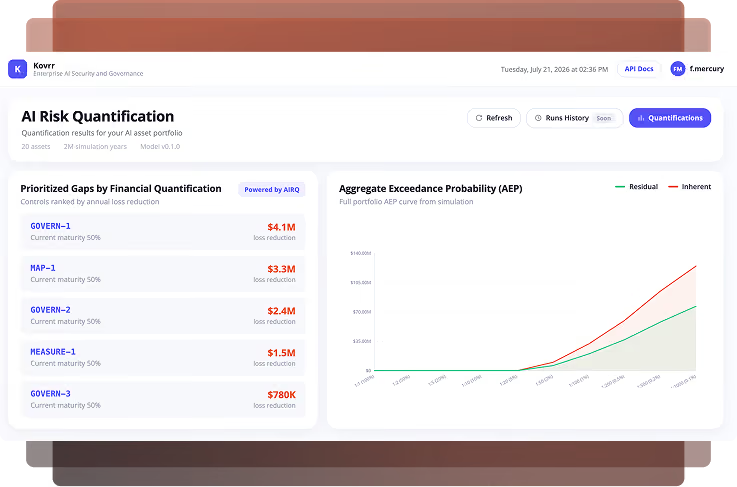
AI Audit Readiness With the Evidence Already Attached
An AI compliance assessment usually begins with a request for evidence that nobody has gathered yet. Kovrr’s AI Security and Governance Platform maps controls against the EU AI Act, NIST AI RMF, and ISO 42001 continuously, so the gaps are known before an auditor asks and the evidence behind each answer is already attached.
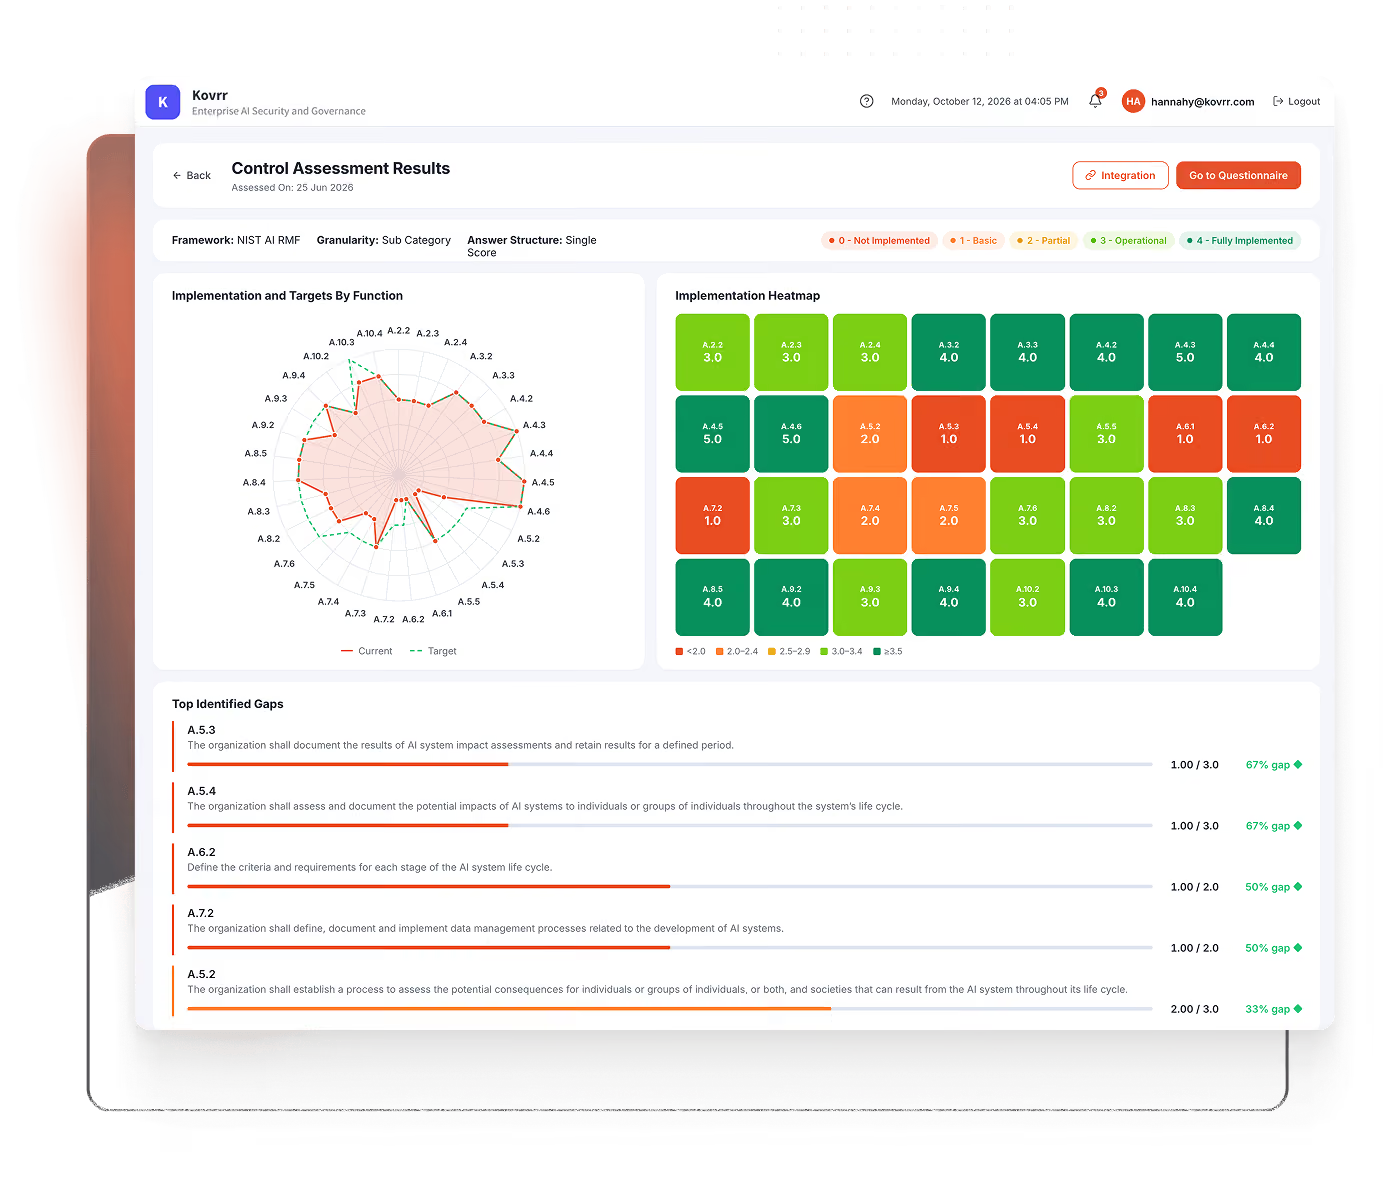
Where AI Compliance Gaps Hide Between Assessments
An AI control assessment answers for the environment on the day it was run, and the environment keeps moving.
1. Terms Change Quietly: Retention periods extend, file upload opens to every workspace user, and SSO enforcement drops for contractors, none of which triggers a reassessment.
2. Frameworks Overlap Unevenly: The EU AI Act, NIST AI RMF, and ISO 42001 ask related questions in different forms, so one control gets documented three times and still leaves a gap.
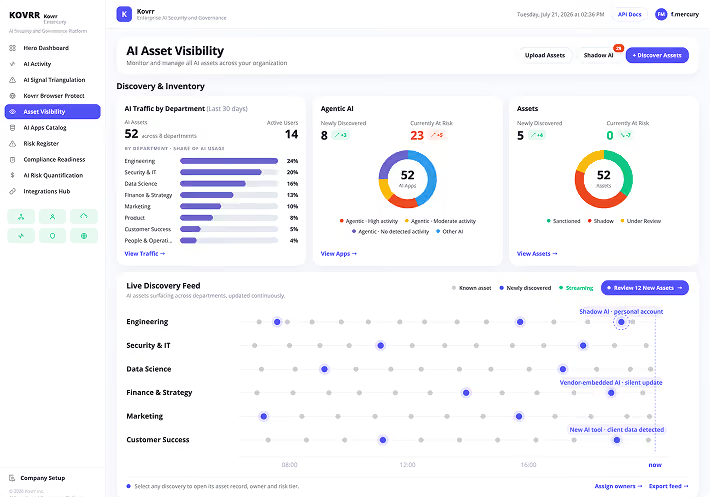
3. New Assets Arrive Unassessed: A tool discovered after the assessment carries no control mapping, no classification, and no evidence behind it.
AI audit readiness holds only where the assessment updates as the environment does.
AI Audit Readiness onthe Kovrr Platform
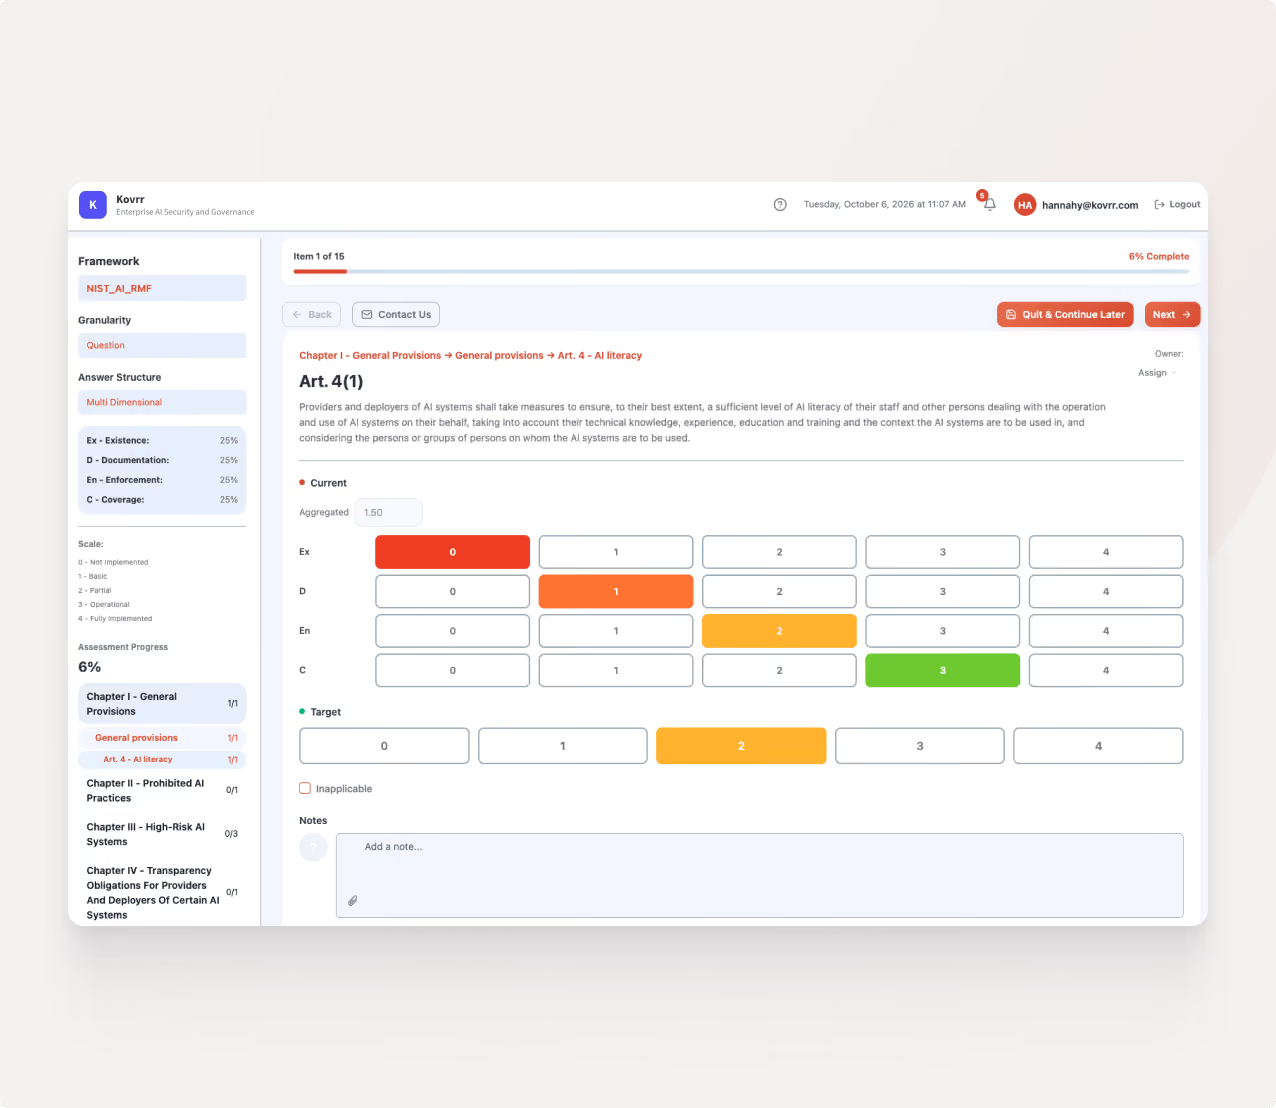
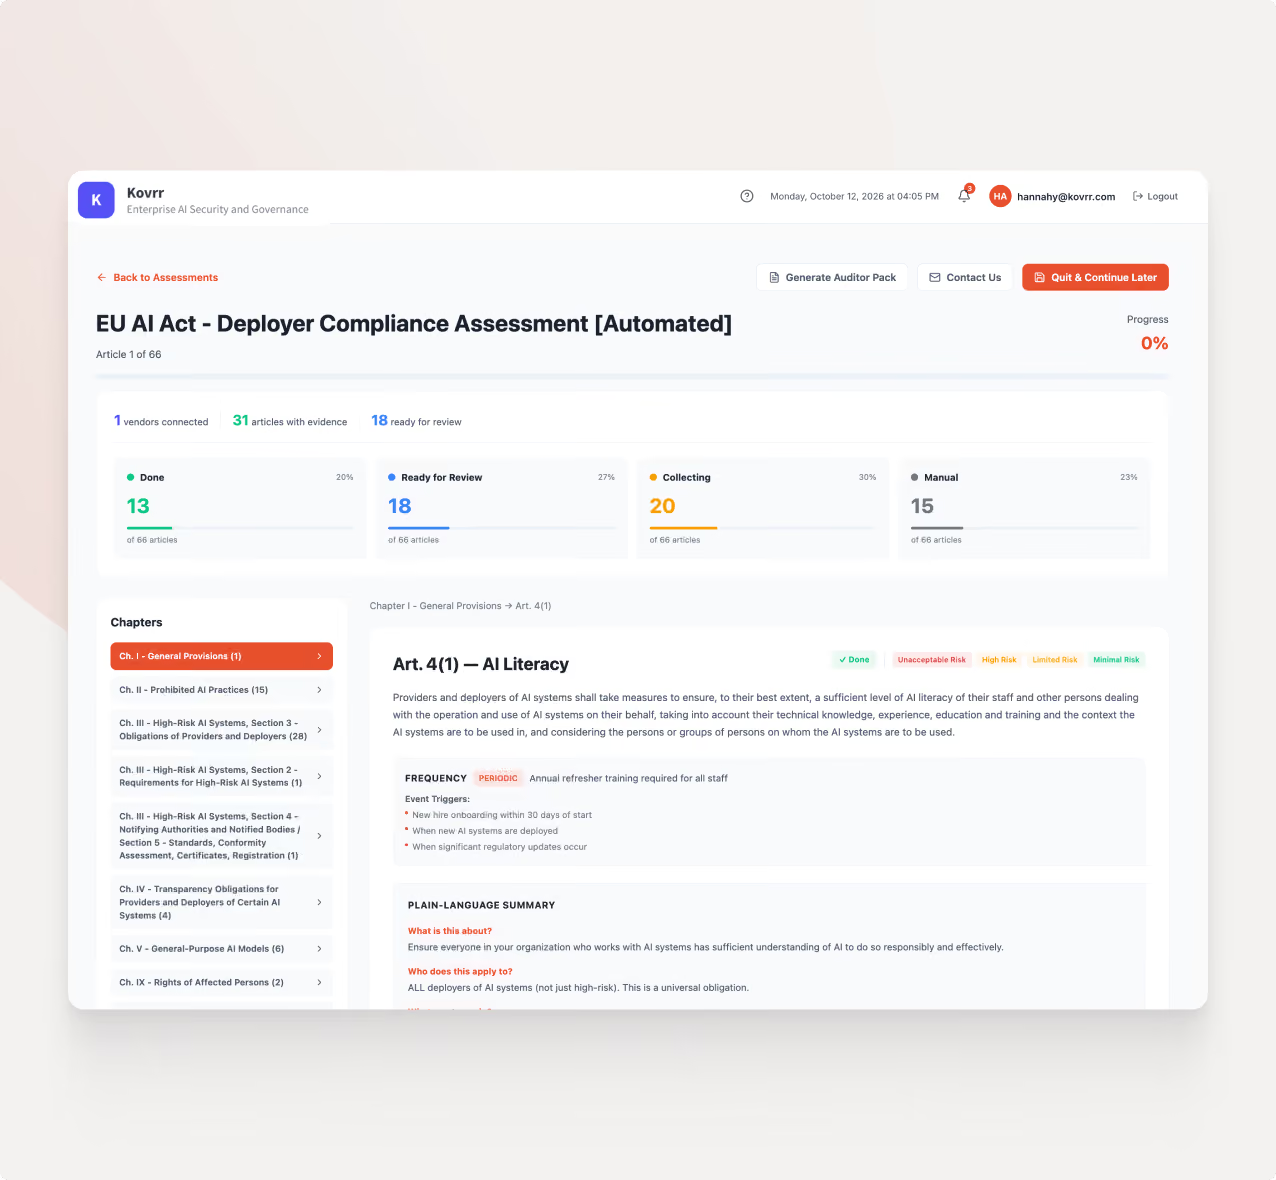
Kovrr maps every AI asset to the controls each framework requires and holds the evidence behind each answer. Gaps surface as the environment changes.
One Control, Every Framework: A single control answer maps across the EU AI Act, NIST AI RMF, and ISO 42001, so overlapping requirements are answered once.
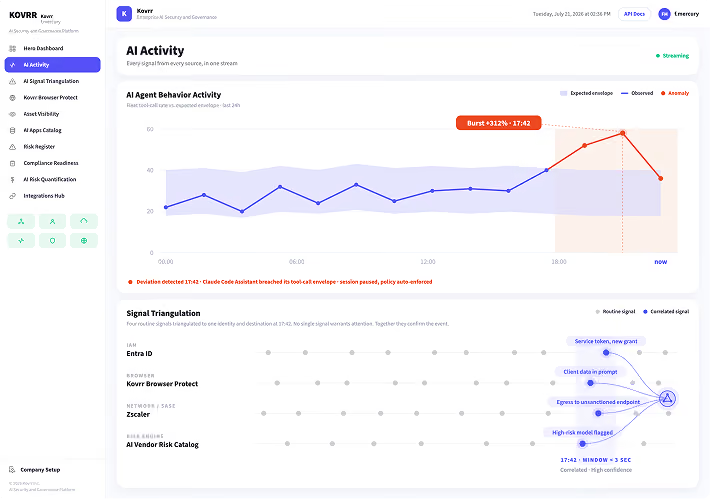
Evidence Attached at the Source: Each control answer carries the telemetry that supports it, which holds when an auditor asks how the organization knows.
Article-Level EU AI Act Coverage: Deployer obligations are assessed article by article, with each one marked done, in review, or collecting.
Agent Actions on the Record: An AI agent audit trail holds what each autonomous action touched and who authorized it, which answers the accountability question frameworks are starting to ask.
New Assets Assessed on Arrival: A newly discovered AI tool enters with its risk classification and control mapping already applied.

Everything your organization needs to go from 0 to EU AI Act Compliant.

The Benefits of Continuous AI Vendor Risk Assessment
AI Audit Readiness FAQs
Schedule a DemoWhat is AI audit readiness?

What are the most common AI compliance gaps?
How does continuous assessment differ from an annual audit cycle?
Which frameworks does Kovrr assess against?
What evidence does an AI audit actually require?
Can agent activity be evidenced for an audit?
