AI Vendor Risk Assessments That Always Reflect the Current Risk
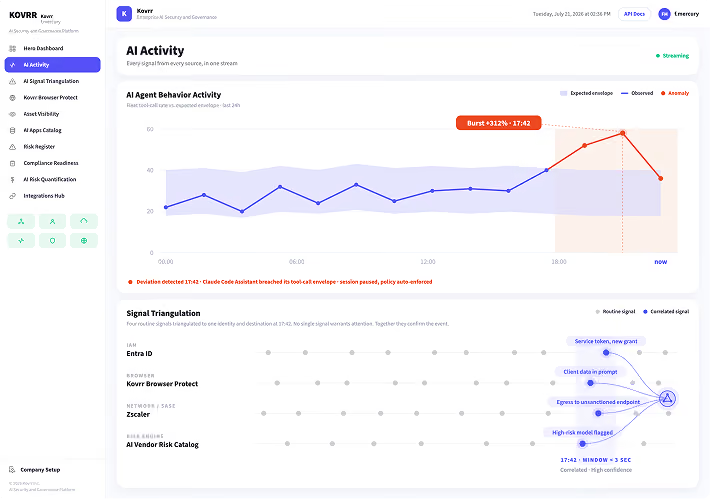
Most AI vendor risk sits with suppliers whose terms changed after the assessment was filed. Kovrr's AI Security and Governance Platform scores providers against a catalog of 15,000+ on training, retention, and agreement terms, and detects when a vendor already under contract starts processing corporate data through a model nobody reviewed.
When Vendor Assessments Expire Faster Than the Contract
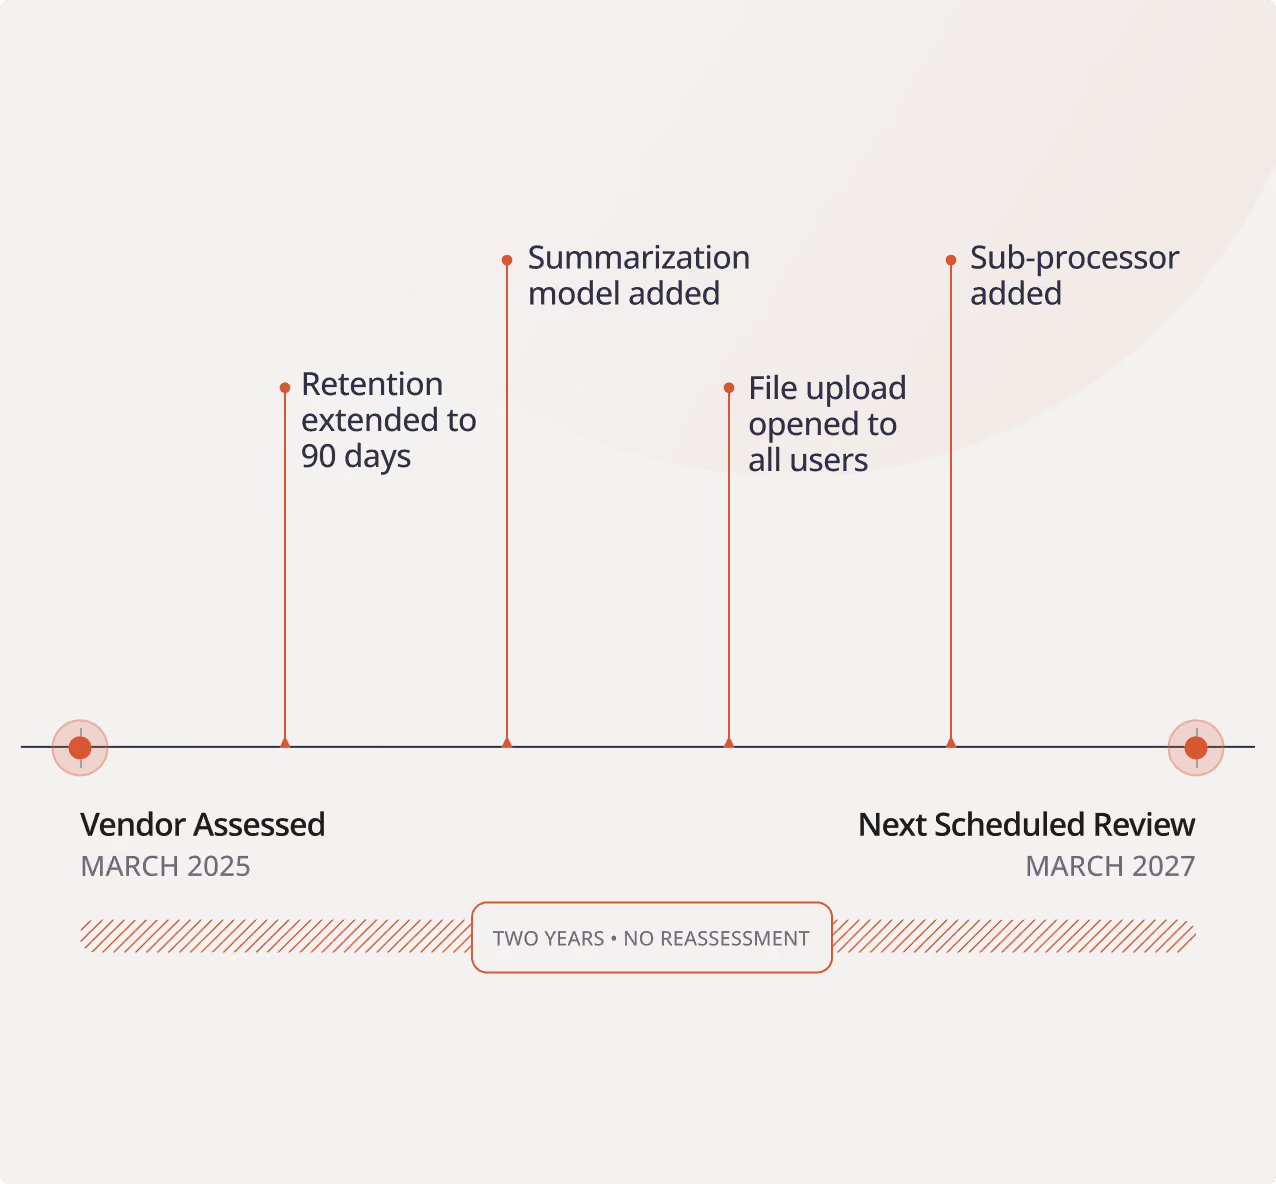
A vendor assessment describes a vendor on the day it was completed, and the contract runs for years. AI vendor risk moves in the meantime.
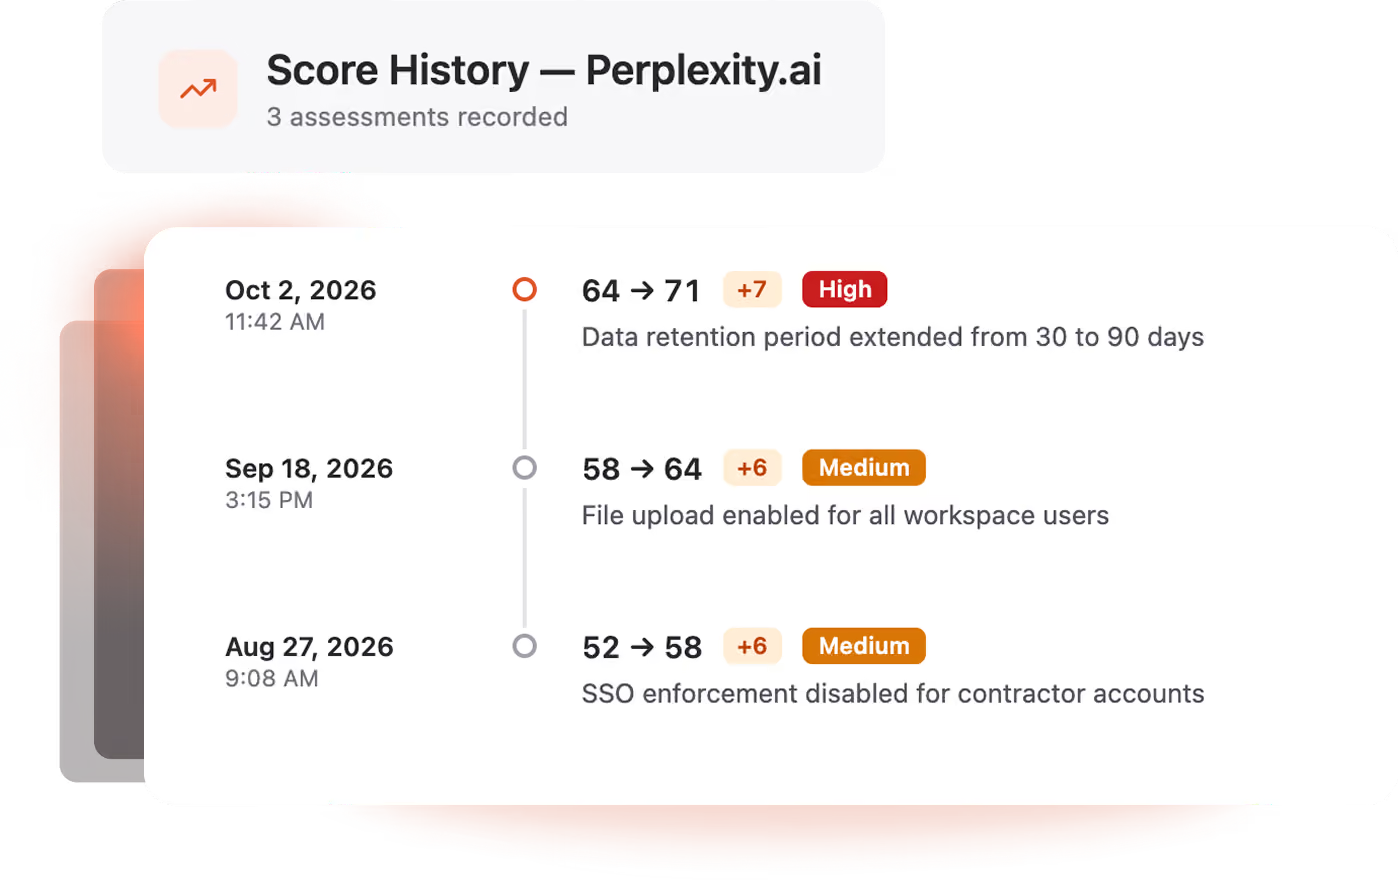
1. Terms Change Quietly: Retention periods extend, file upload opens to every workspace user, and SSO enforcement drops for contractors, none of which triggers a reassessment.
2. AI Arrives Later: A supplier approved for a non-AI product adds a model to it, and the risk profile on file describes a product that no longer exists.
3. The Chain Extends: A vendor adds a sub-vendor, and the AI processing corporate data sits two relationships away from anything that was reviewed.
AI vendor risk assessment holds only where the score moves when the vendor does.
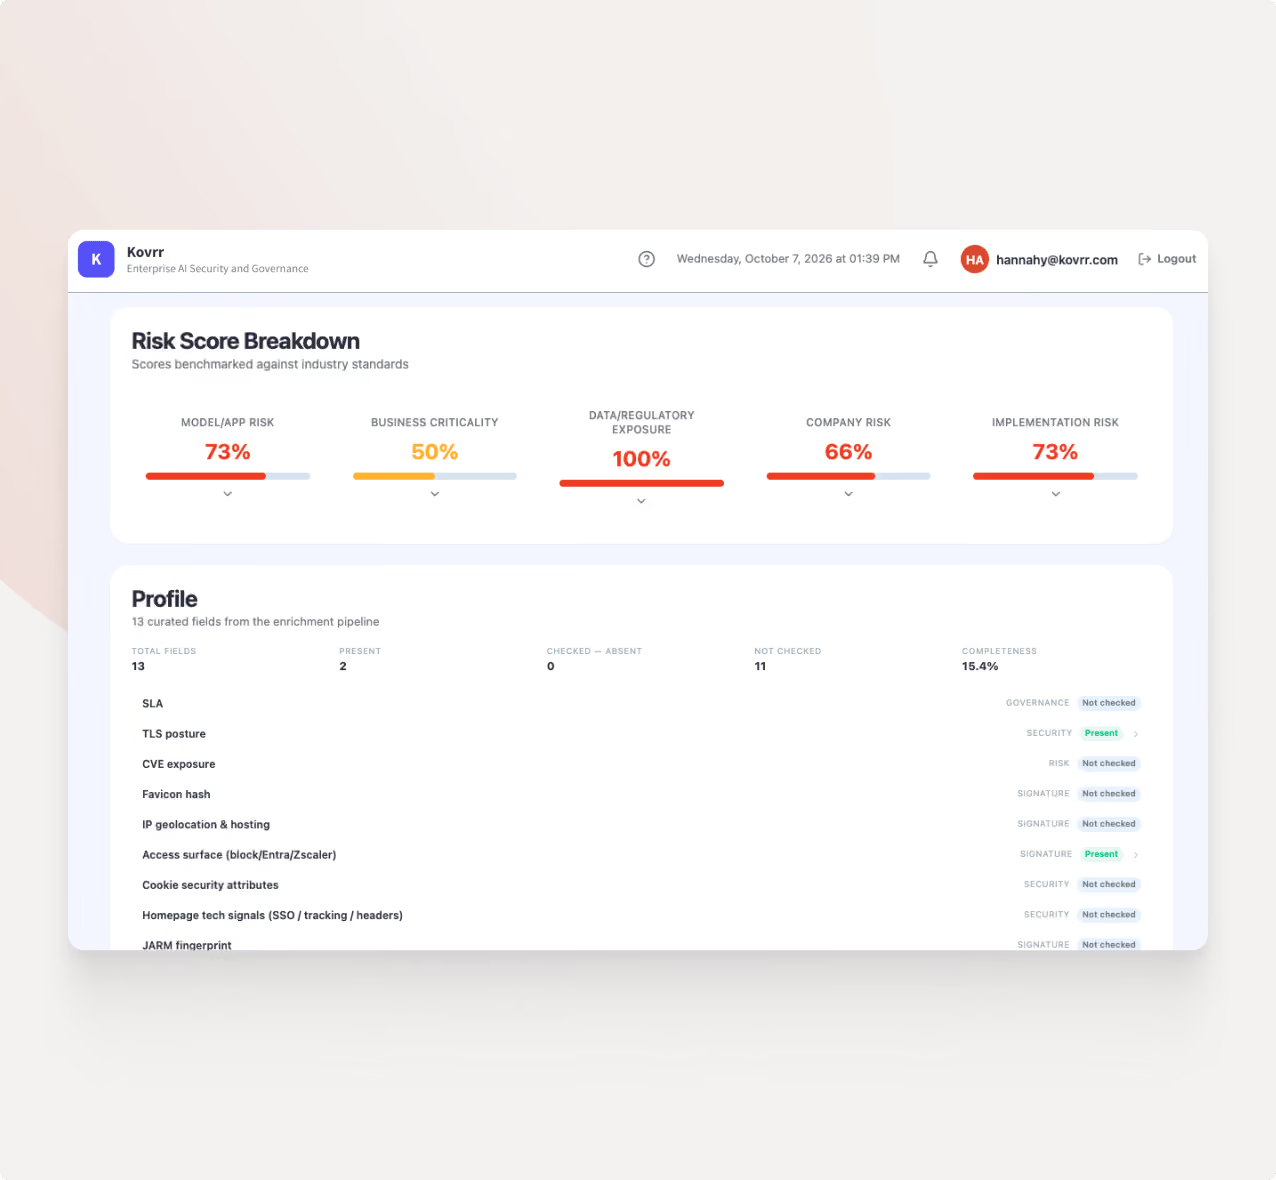
How Kovrr Assesses AI Vendor Risk
Kovrr scores vendors against observed behavior rather than a questionnaire. Each provider carries a risk score across multiple dimensions, updating when the vendor changes.
Scoring Across Five Dimensions: Model and app risk, business criticality, data and regulatory exposure, company risk, and implementation risk each carry their own score.
A Catalog of 15,000+ Providers: Vendors arrive already scored, so an assessment starts from existing intelligence rather than an outbound questionnaire.
Terms Resolved, Not Assumed: Training, retention, and agreement status are held per vendor, which scopes exposure when regulated data reaches one.
Change Detected at the Source: A vendor altering retention, access, or model use moves its score, with the reason recorded against the date.
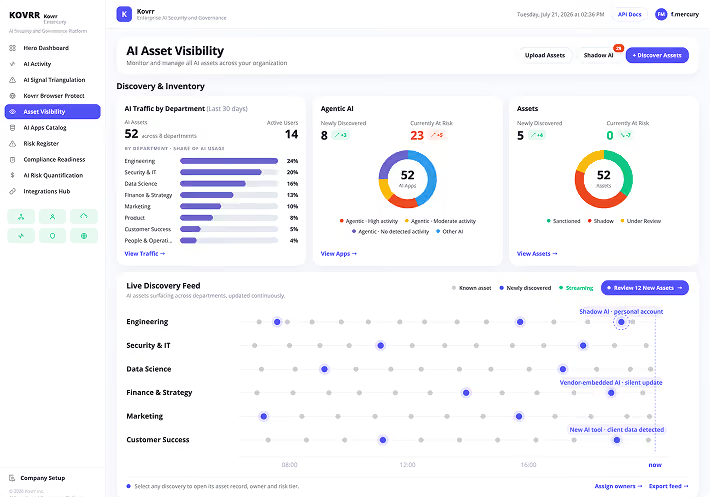
Vendors Found Through Use: Providers reaching corporate data surface through telemetry, including the ones no procurement record holds.

Search Inside the AI Vendor Risk Catalog
The catalog holds continuously updated profiles on 15,000+ AI providers, covering risk signals across five dimensions, regulatory exposure, incident history, and security certifications. Schedule a call to get complimentary access and look up the vendors already in the environment.

The Benefits of Continuous AI Vendor Risk Assessment
AI Vendor Risk Assessment FAQs
Schedule a DemoWhat is AI vendor risk assessment?

How often should AI vendors be reassessed?
What about vendors that added AI after they were approved?
Does assessment cover sub-processors
What does a vendor risk score include?
How does vendor risk connect to financial exposure?
