What Is a Cyber Security Risk Assessment? Six Steps, in Plain Terms


What is a cyber security risk assessment?
It is a structured process, not a guess, for finding the risks that matter most, estimating how likely each one is, and measuring how much damage it could do. It answers two questions: how much risk do we have, and which risks should we fix first?
What are the six steps of a cyber security risk assessment?
First, identify your assets. Second, identify threats and vulnerabilities. Third, calculate the risk. Fourth, prioritize and plan. Fifth, implement and measure. Sixth, reassess on a schedule.
Is the goal of a risk assessment to get to zero risk?
No. With limited time and budget, the goal is to decide what to do with each risk: accept it, reduce it, or transfer it. Prioritizing helps you focus on the scenarios that are most likely or most costly, and compare the cost of each control against the risk it reduces.
How often should you reassess cyber risk?
Regularly, on a schedule. Quarterly is a common cadence, and each cycle builds on the last. Your attack surface keeps growing as you add cloud services, remote work, and third-party vendors, so a one-time assessment goes stale.
How does cyber risk quantification (CRQ) fit into a risk assessment?
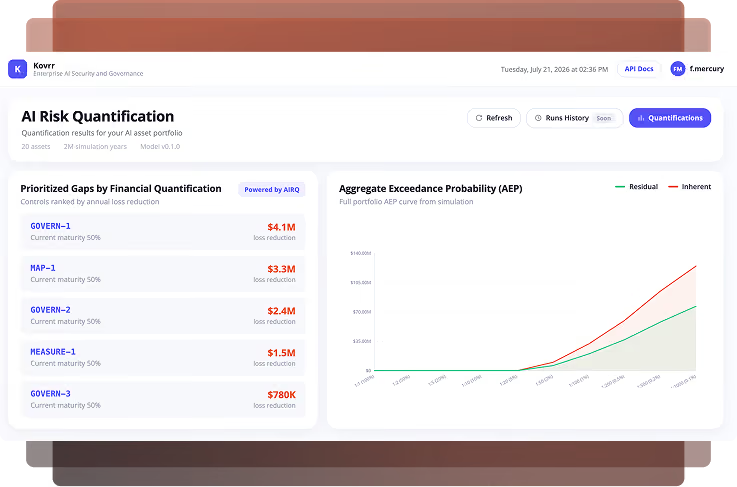
Risk matrices are a start, but putting numbers on impact gives a clearer picture. CRQ translates threats into financial terms: expected losses, the chance of exceeding an amount, and return on investment. Tracked over time, it lets the board see exposure move quarter over quarter.


