Agent Hijacking
Agent hijacking is an attack in which manipulated input redirects an AI agent away from its assigned task, so the agent continues operating under its own legitimate permissions while pursuing an objective it was never given.
The Agent Keeps Working, for Someone Else
Hijacking changes what an agent is trying to accomplish while leaving everything else intact. Credentials stay valid, the session stays open, and activity continues at a normal rate against systems the agent reaches every day. Detection built on anomalous access patterns finds nothing, because the access is not anomalous. What changed is the objective, and objectives do not appear in access logs.
Injection Is the Common Entry Route
An agent asked to triage support tickets reads a ticket containing instructions addressed to it. An agent summarizing a repository encounters a comment written for the model instead of the reader. Both cases run through indirect prompt injection, where the payload arrives inside content the agent was told to process. Longer-running agents are more exposed, since every document they touch is another opportunity.
Persistence Separates Hijacking From a One-Off Injection
A single injected instruction produces a single bad action. Hijacking persists when the manipulated goal enters memory, a scratchpad or a task queue the agent reads on each cycle, so the agent re-adopts the objective after the originating content is long gone. Clearing the context the agent is running in becomes part of containment, which AI incident response has to account for.
Detection Depends on Goal-Level Evidence
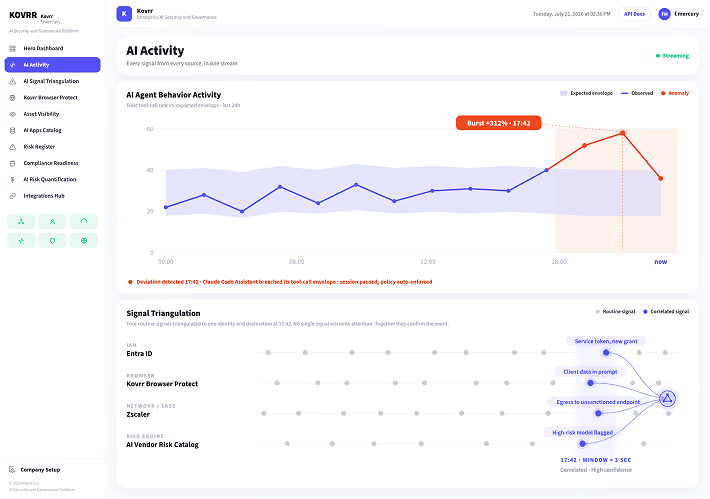
Catching a hijack requires comparing what an agent was asked to do against what it then did, which means the assigned task has to be recorded alongside the actions. An AI agent audit trail that captures task context supports that comparison. Narrowing permissions limits the damage a hijacked agent can produce, since the attacker gains exactly the access the agent holds and nothing more.
Related Terms

Full AI Visibility. Full Control. One Connected Platform.
Enterprise AI is expanding faster than most governance programs can track. Kovrr connects every AI signal across browser, endpoint, network, identity, and vendor systems into a single platform so security, governance, and risk teams work from the same evidence.