What Is a NIST Assessment? Risk vs. Maturity, Explained


What is a NIST assessment?
NIST publishes free, public, voluntary guidance, and a NIST assessment measures your organization against it. In practice, it usually means one of two things: a risk assessment or a maturity assessment. It often comes up when a customer security questionnaire asks, "Are you NIST compliant?"
What is the difference between a NIST risk assessment and a maturity assessment?
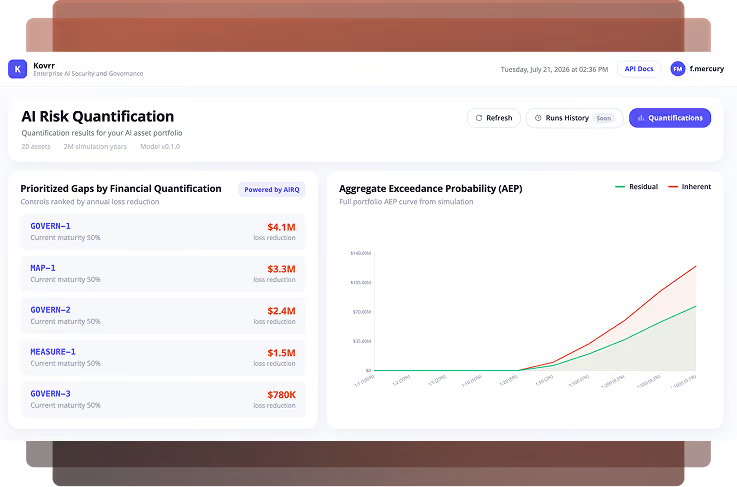
A risk assessment follows NIST SP 800-30 and walks you through threats, likelihood, and impact. A maturity assessment uses the NIST Cybersecurity Framework to score how mature your controls are. Decide which one answers your question first: assess specific risks, or score your controls.
Is a NIST assessment a certification?
No. NIST guidance is voluntary, and an assessment measures you against it rather than certifying you. The video covers what the results depend on.
What do you get out of a NIST assessment?
A gap list and a plan. The gaps show where your risks or controls fall short, and the plan sets out what to do about them.


