Blog Post
The Best Identity Security Vendors for AI Agents
October 29, 2026
Every major identity vendor shipped an agent offering during 2026, and the datasheets converge on the same three claims. Agents get first-class identities, permissions are scoped, and access is governed.
The question that separates them is narrower. When the engineer who built an agent leaves the company, what happens to the agent? The answers differ enormously, and they differ for reasons that trace back to what each vendor was originally built to do.
Why Does a Departure Break an Agent?
Because the agent was never an object in the process that handles departures.
The Mechanism
Joiner, mover and leaver workflows act on people. An engineer provisions an agent during a project, frequently using their own credentials or a personal key tied to their corporate account, and nothing records that a second actor now depends on that identity. The leaver process runs against the human and the agent is invisible to it.
Two Failure Modes, Opposite Directions
Deprovisioning the human either breaks the agent, because the credential it authenticated with has gone, or leaves the agent running on authority that now belongs to nobody. Which one occurs depends on whether the agent borrowed a credential or held its own.
Why Both Are Bad Differently
The first is a production outage nobody predicted and somebody will notice within hours. The second is an orphan with standing access that nobody notices at all, and an agent whose builder already left is the case that persists.
What Should the Evaluation Ask?
One question that cuts through the feature lists.
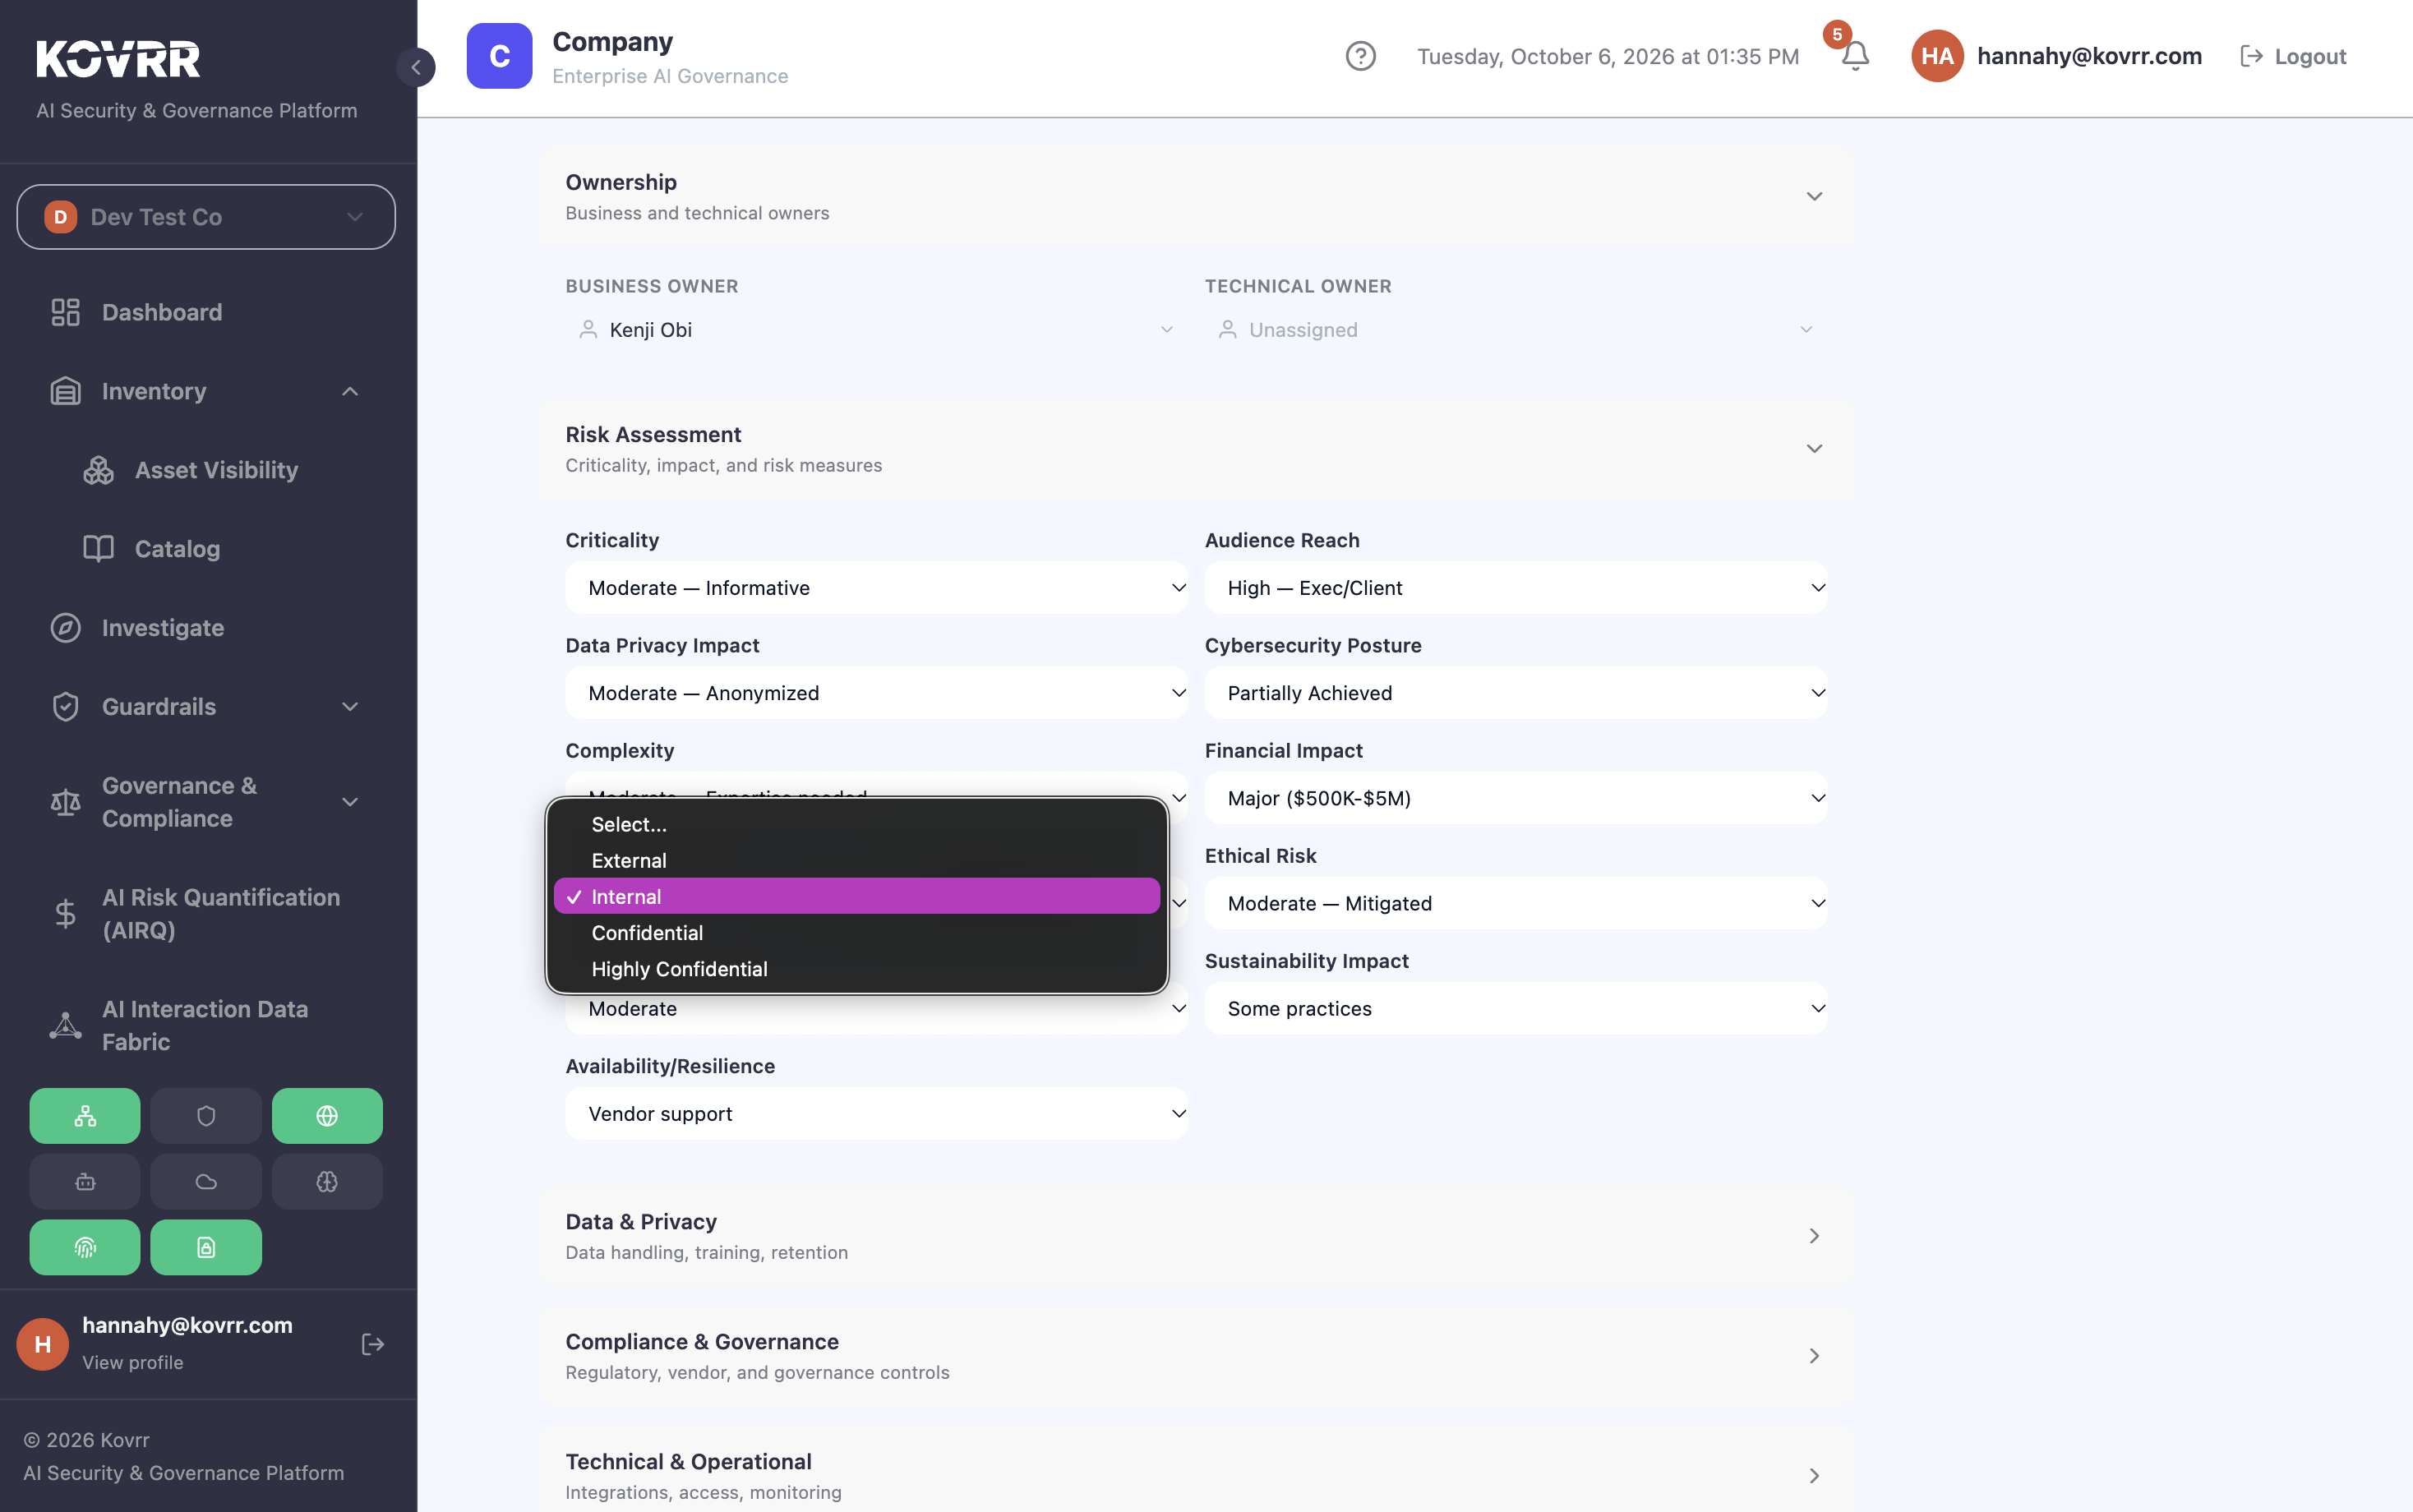
Is the Agent an Object in the Leaver Workflow?
Not whether the platform supports agent identities, which every vendor now answers yes to. Whether deprovisioning a person triggers a decision about the agents that person created, naming them and requiring somebody to transfer, retire or confirm each one.
The Supporting Question
Whether an agent can exist without an owner who is distinct from its builder. A platform permitting that will reproduce the problem with every departure, regardless of how well it issues credentials.
How to Test It
Create a test agent under one account, then run that account through the leaver process and observe what the platform does. The result is more informative than any datasheet.
How Does Vendor Heritage Decide the Answer?
Four lineages, each strong where its original problem overlapped with this one.
Governance Platforms
SailPoint comes from identity governance and administration, where joiner, mover and leaver is the core competence rather than an extension. Its Agentic Fabric adds shadow AI discovery, detection and response for non-human identities, dynamic access certifications and a kill switch. The lineage maps directly onto the departure problem.
Privileged Access Platforms
CyberArk comes from privileged access and secrets management, and its agent work focuses on generating dynamic, short-lived secrets rather than long-lived keys, which addresses the credential axis directly, since a short-lived secret cannot be inherited by an orphan, and it says less about discovering agents nobody registered.
Directory and Workforce Platforms
Microsoft Entra Agent ID extends conditional access and continuous threat protection to agents, with native integration into its own agent-building tooling. Okta's blueprint adds agent discovery through posture management and certification workflows built for machine speed. Both are strongest where the agent lives inside their ecosystem.
What Do the Specialists Add?
Coverage of the agents the incumbents do not know exist, which is the population that causes the departure problem in the first place.
- Discovery and mapping: Reco and Token Security scan cloud and software estates to inventory agents and map each back to a human owner.
- Runtime authorization: PlainID and Aembit evaluate the agent, the request and the human context at the moment of access rather than at provisioning.
- Runtime issuance: Composio creates and scopes agent credentials programmatically, with termination built into the issuance.
Why Discovery Matters Most Here
An agent created outside any governed process is the one that will be orphaned, because it is absent from the system that would otherwise notice. Mapping each agent back to a named human is what makes the departure question answerable at all.
Why Runtime Authorization Changes the Shape
Where authority is evaluated per request rather than granted at provisioning, a change in the human's status propagates immediately rather than waiting for a review cycle. The orphan window closes on its own.
How Should Permission Scoping Be Judged?
Judge it on what the agent can reach rather than on what the policy says, since the two diverge under inheritance.
The Inheritance Problem
An agent running under a person's credential holds that person's authority, including grants issued years ago for systems nobody associates with the work. Scoping the agent means scoping what it inherits rather than configuring the agent itself.
What Separates Platforms
Whether an agent identity can be created with less authority than its creator holds. A platform that can only mirror the creator's permissions has not scoped anything, and managing agent identity at scale depends on that separation existing.
The Ceiling Worth Setting
A maximum authority per agent, set below what any human creator could grant. Access control applied at the agent level is what makes the ceiling enforceable rather than advisory.
Should an Organization Buy One or Several?
Several, usually, which is how these products are deployed in practice.
The Layering Pattern
Directory platforms issue identity, privileged access platforms handle the secrets, governance platforms run certification and the leaver process, and specialists supply discovery and runtime decisions. Each layer answers a different question and none answers all four.
What That Does to a Shortlist
Work out which layer is weakest before comparing vendors within it. An organization with strong directory coverage and no discovery is shopping in a different category from one with the reverse, and why agent identity matters covers the foundations beneath all four.
What Should Be Established?
Three things, and the first is a test rather than a question.
Run one account holding a test agent through the leaver process and record what happens, since that answer is not on any datasheet. Count how many existing agents have an owner distinct from their builder, because the difference is the population at risk from the next departure. Then establish whether an agent identity can be created with less authority than its creator holds, as a platform that can only mirror permissions has not scoped them. Governing agents at the boundary covers enforcement once identity is settled, and the agent security vendor comparison covers the runtime protection layer rather than the identity one.
Test the Departure, Not the Datasheet
Every identity vendor now claims first-class agent identities, scoped permissions and governed access, so the claims no longer separate anybody. What separates them is whether an agent is an object in the leaver workflow, since a departure either breaks an agent whose borrowed credential vanished or orphans one holding authority that belongs to nobody. Vendor heritage predicts the answer, with governance platforms strongest on the departure itself, privileged access platforms strongest on credentials, and directory platforms strongest inside their own ecosystems. Specialists cover the agents nobody registered, which is the population that gets orphaned. Most organizations end up layering several rather than choosing one.
To see which agents exist, who owns each one and what they can reach, book a demo mapped to your own estate.
Agent Identity Vendor FAQs
Speak to an ExpertWhat happens to an AI agent when its builder leaves the company?

Why do leaver workflows miss AI agents?
What should an agent identity evaluation test?
How does identity vendor heritage affect agent capability?
How should agent permission scoping be judged?
Should organizations buy one agent identity platform or several?