AI Acceptable Use Policy
An AI acceptable use policy is the document stating which AI tools employees may use, under which accounts, what categories of data may be submitted to them, and which outputs require human review before acting.
A Usable Policy Names Tools and Data Categories
A policy that tells employees to use AI responsibly decides nothing. The version people can follow names sanctioned tools individually, distinguishes a corporate tenant from a personal account on the same service, lists the data categories that may never be submitted, and states which outputs need review before anyone acts on them. Kovrr's guidance on building and enforcing an AI acceptable use policy works through each of those sections.
Prohibition Alone Produces Shadow AI
A policy banning everything unsanctioned, published to a workforce under deadline pressure, moves usage somewhere unobserved instead of stopping it. Employees reach for the tool that does the job, and personal accounts leave no corporate record. The policies that hold up pair a short prohibition list with a workable sanctioned path, which keeps usage where it can be seen and reduces the shadow AI surface rather than relocating it.
Named Tools Date Faster Than the Review Cycle
An allowlist written against specific products goes stale within a quarter, since vendors ship AI features into software already deployed and new assistants arrive weekly. Policies that survive are written against capabilities and data categories, with the tool list maintained as a living register underneath. The annual review cycle most policies inherit from older governance work is the wrong cadence for this subject.
A Policy Nobody Can Observe Cannot Be Enforced
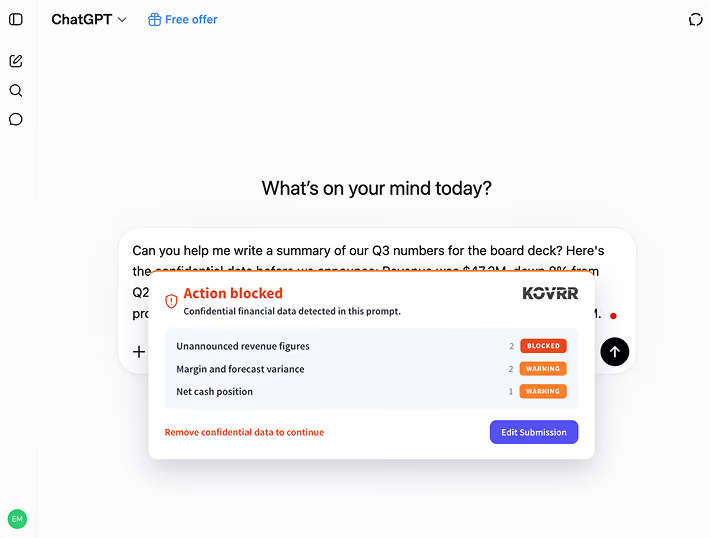
Stating a rule and detecting its violation are separate problems. Enforcement positioned at the moment of submission, before content leaves the device, is covered under policy enforcement before the prompt is sent, and the broader governance structure the policy sits inside is covered under AI policy. Auditors asking for evidence of enforcement want records of the exceptions, not a copy of the document.
Related Terms

Full AI Visibility. Full Control. One Connected Platform.
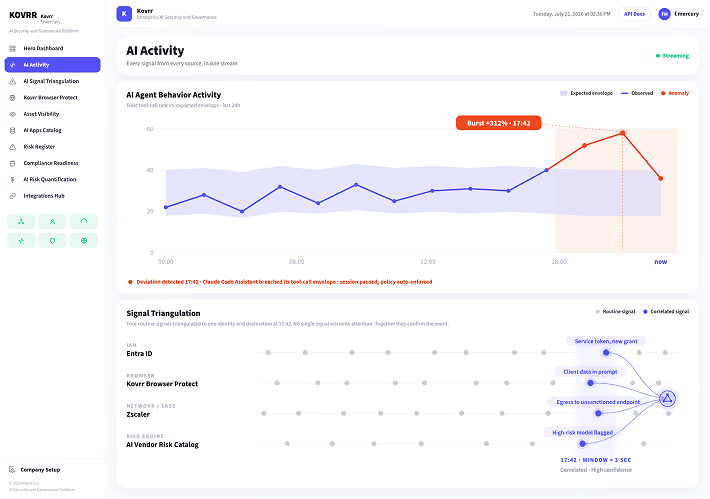
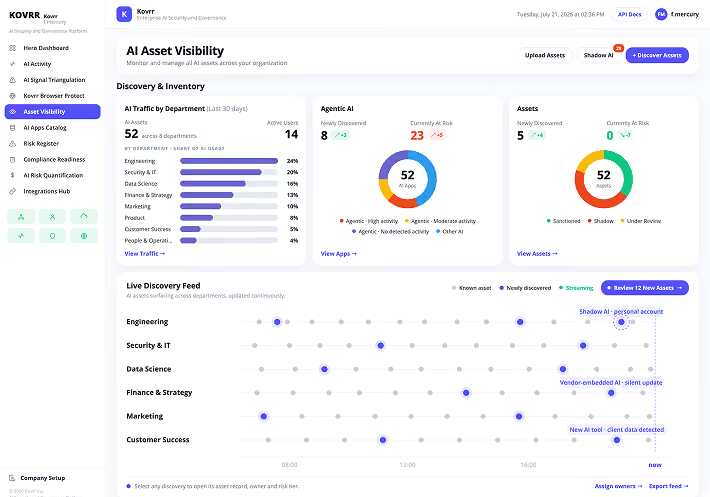
Enterprise AI is expanding faster than most governance programs can track. Kovrr connects every AI signal across browser, endpoint, network, identity, and vendor systems into a single platform so security, governance, and risk teams work from the same evidence.