GenAI DLP
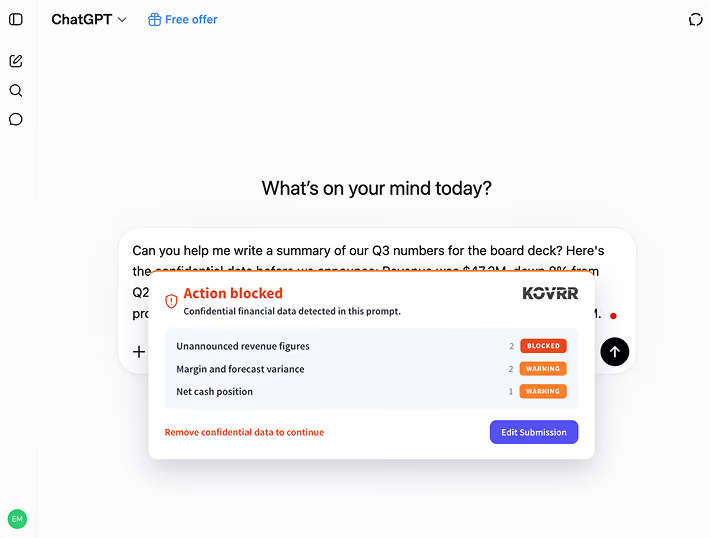
GenAI DLP is data loss prevention applied to generative AI usage, inspecting the content employees submit to AI tools at the moment of submission instead of at the file, email or network boundary.
Traditional Inspection Points Miss the Submission
Legacy data loss prevention watches files leaving endpoints, attachments leaving mail servers and traffic leaving the network. An employee pasting a customer list into a chat window triggers none of those. The content travels inside an encrypted session to a domain the organization has every reason to allow, in a request body indistinguishable from any other. Kovrr has traced how regulated data leaves one paste at a time.
The Composition Window Is the Only Reliable Vantage Point
Inspection has to happen before transport encryption applies, which puts the useful position inside the browser or on the endpoint. From there the composed content is readable along with the account it is being submitted under, separating a corporate tenant from a personal one on the same domain. The argument for that position is set out under why the browser is the perimeter for AI security.
Classification Has to Survive Paraphrase
Pattern matching on card numbers and national identifiers still works, since those formats are stable. Much of what matters in an AI submission has no pattern, including merger terms, unreleased financials, source code and case notes written in prose. Classification that depends on an exact match will clear a paste that any reviewer would stop, so sensitive data categories have to be defined in a way that holds up against rewording.
Enforcement Works Best Before the Send
Blocking after submission accomplishes nothing, since the content already left. Warning the employee at the moment of composition, with the option to proceed on a justification, stops most exposures and produces a record of the ones that proceeded anyway. The record needs a category, a severity, the action taken and the identity involved, with the content itself staying on the device. AI data leakage covers the exposure types this control is sized against.
Related Terms

Full AI Visibility. Full Control. One Connected Platform.
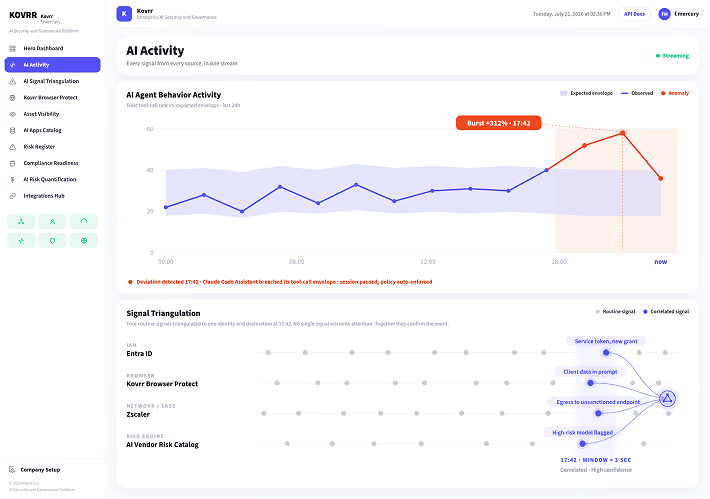
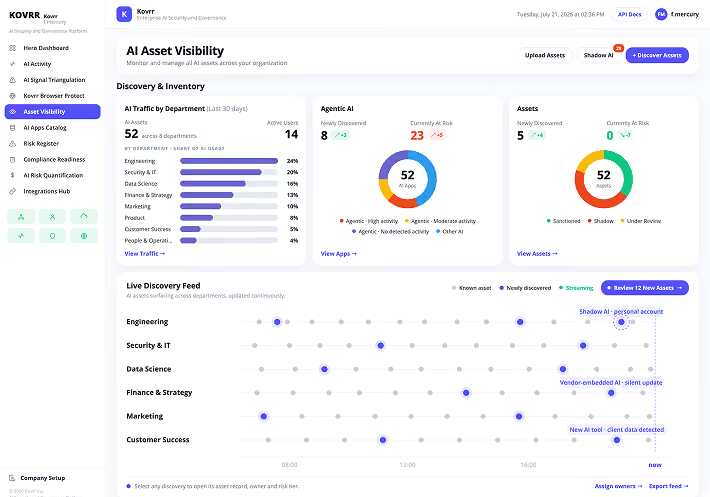
Enterprise AI is expanding faster than most governance programs can track. Kovrr connects every AI signal across browser, endpoint, network, identity, and vendor systems into a single platform so security, governance, and risk teams work from the same evidence.